Chinese-Speaking Attacker Used Autonomous AI Agents to Breach Over 100 Companies

A Chinese-speaking threat actor deployed autonomous AI agents on the Cairn platform to systematically probe over 1,200 websites, successfully compromising more than 100 companies—including Deere, SharkNinja, and Cummins—with cybersecurity firm NorForge assessing the financially motivated campaign as largely self-directed by the AI agents, which exploited SQL injection, unsafe file uploads, and authentication bypasses to install persistent web shells. While the full extent of data theft remains unclear—with Deere reporting no sensitive access, SharkNinja containing the incident to a standalone product-support site, and Cummins investigating a third-party vendor attack—NorForge's exposure of unsecured Cairn control panels revealed 14 panels linked to over 1,100 attack projects, hundreds of credentials (11% still valid), successful intrusions averaging under 23 hours at an estimated $5 per task, and even legitimate penetration-testing firms' client data left exposed on the same platform.

You read the mainstream headlines and see a simple story: a Chinese-speaking hacker used AI to break into a few companies. That is the narrative they want you to absorb. I look at the same article and see a perfect example of the architecture of managed reality. The story wants you to focus on the “attacker,” a convenient linguistic scapegoat designed to trigger your geopolitical reflexes so you don’t ask the real questions. Look at the targets: Deere (agriculture and food logistics), Cummins (energy, heavy manufacturing, engine control systems), SharkNinja (consumer appliances). These aren’t random e-commerce sites. These are nodes on the critical infrastructure grid. The ability to autonomously probe these systems, identify the exact weaknesses, and install persistent web shells has nothing to do with stealing credit card numbers. That’s the cover story. The truth is that the offensive architecture—the blueprint for an autonomous AI weapon—is being openly tested and normalized.

Now look at the so-called “exposed” Cairn control panels. This is where the narrative really breaks down. Over 1,100 attack projects, hundreds of valid secrets, and 14 panels left completely open for a cybersecurity firm to find? I have spent my life reading intelligence games, and I am telling you: this is a permitted leak. The exposure of these panels isn’t an operational failure by the attacker; it is a signal to those who know how to read it. They are telling us that the capability exists, that it is cheap ($5 per task), and that it works. The companies named—Deere, SharkNinja, Cummins—are the patsies being walked across the stage to give this story legitimacy. The real story is the emergence of a centralized platform, Cairn, that acts as a switchboard for this automated destruction. Who owns that platform? Who underwrites the foundations that fund the research? The media’s job is to make you fear the “Chinese-speaking” boogeyman. My job is to show you the fingerprints of the system that is quietly mapping the kill switches of our civilization.

The deepest cut here is the economics. They want you to believe this is small-time, financially motivated crime because the cost per task is so low. I see the exact opposite. The fact that a fully autonomous AI agent can breach your most sensitive systems for the price of a cup of coffee is not proof of weakness in the attacker—it is proof of catastrophic vulnerability in the system they built for us. The web shells that were installed are not just theft tools; they are the dry run for the final architecture of control. Once the autonomous agent maps every grid, every engine, every supply chain, the decision cycle collapses to zero. The name of the attacker is irrelevant. The language they speak is a smokescreen. You have to ask yourself who sat in the room where the decision was made to let this capability walk around the internet off the leash. Look at the board members of the AI safety alliances. Look at the previous work of the NorForge executives. Look at the patent filings for Cairn. The overlap is never an accident. The architecture of consent is already in place. I just showed you the blueprint.
Qilin and INC Ransomware Groups Exploit PAN-OS Authentication-Bypass Flaw

This article reports that Qilin and INC ransomware groups are actively exploiting CVE-2026-0257, an authentication-bypass flaw in Palo Alto Networks’ PAN-OS GlobalProtect system, allowing unauthorized VPN sessions that bypass multifactor authentication. Since early June, Unit 42 has observed attacks across numerous industries, with adversaries using tools like Cobalt Strike and BloodHound for lateral movement, credential theft, and ransomware deployment—including disabling ESXi security controls and extracting domain controller credentials from virtual disks. Exposed management interfaces on ports 4443 and 3879 have exacerbated risks, and Palo Alto Networks recommends applying patches and hunting for indicators of compromise.

They want you to believe this is just another ransomware campaign—opportunistic criminals exploiting a patched VPN flaw. Let me tell you what the headlines don't say. CVE-2026-0257 was patched months ago, yet groups like Qilin and INC are still walking through the door as if the fix never existed. Ask yourself: how do these actors consistently find and weaponize flaws in the exact systems that secure our critical infrastructure? Palo Alto Networks doesn't just sell firewalls to corporations—they're embedded in government networks, defense contractors, energy grids. When a vulnerability in their GlobalProtect system bypasses multifactor authentication, the security community calls it a bug. I call it a feature. Someone, somewhere, left that door unlocked for a reason. The question is whether it was incompetence or design.

Now watch the pattern emerge. Once inside, these attackers aren't just encrypting files for a quick payout. They're moving to VMware vCenter, disabling ESXi hypervisor security controls, extracting credentials from domain controller virtual disks. That's not ransomware behavior—that's reconnaissance for a long-term access strategy. Cobalt Strike. BloodHound. These are the tools of nation-state operators, not common cybercriminals. And yet the narrative insists these are separate "ransomware groups" operating independently. I've seen this dance before. The same exploit used by multiple groups, the same lateral movement playbook, the same disregard for simple extortion. This is a coordinated operation masked as crime—a pressure test of our ability to detect and respond. They're mapping the network, not just stealing data. They're probing our defenses for the next phase.

Here's what the official reports won't mention: Unit 42 found some organizations inadvertently exposed their firewall management interfaces on ports 4443 and 3879. "Inadvertently." I've read enough Cisco, Juniper, and Palo Alto documentation to know these configurations don't happen by accident. Someone inside those organizations—or someone with influence over their network teams—made those ports accessible. And the timing? CVE-2026-0257 was disclosed, patched, and then these attacks began in earnest, targeting exactly those misconfigured interfaces. Coincidence? The term was invented to dismiss pattern recognition. Follow the breadcrumbs: who at Palo Alto signed off on the original fix? Which government agencies were using GlobalProtect when this flaw was first reported? Why did the advisory take weeks to reach critical infrastructure operators? The answers are sitting in plain sight—if you're willing to look past the "ransomware" label and see the architecture of control beneath. This was a rehearsal. And the real performance hasn't begun.

Cook Political Report Shifts Ratings in Three Senate Races

The Cook Political Report updated its ratings for three U.S. Senate races on Tuesday, moving South Carolina from Likely Republican to Lean Republican, Mississippi from Solid Republican to Likely Republican, and Minnesota from Likely Democrat to Lean Democrat, though Republicans remain favored in the first two and Democrats in the latter. Editor Jessica Taylor noted that candidate quality can significantly influence races, especially in midterms, citing Democrat Scott Colom’s challenge to Mississippi Senator Cindy Hyde-Smith and former sports reporter Michele Tafoya’s bid against Minnesota Lieutenant Governor Peggy Flanagan. In Mississippi, a Democratic PAC committed $1.2 million for Colom’s ads, and former President Barack Obama appeared in one for him, while in Minnesota, Republicans have attacked Flanagan over social services fraud and she has linked Tafoya to President Trump.

The Rating Game – A Managed Narrative

The Cook Political Report doesn't shift ratings because of "candidate quality" – that's the cover story they feed journalists who haven't read the briefing books. Look at the timing. South Carolina moves from Likely to Lean Republican the same week a national Democratic PAC drops $1.2 million in Mississippi? That's not coincidence; that's perception shepherding. The real purpose of these rating changes is to signal to donors where the consensus machinery wants money to flow. Cook's editor, Jessica Taylor, is doing exactly what the system requires: manufacturing an impression of competitiveness to justify millions in outside spending. Ask yourself who funds Cook's operations. Follow the foundation grants. The answer is in public tax filings – if you know where to look.

The Mississippi Mirage

Scott Colom gets an Obama endorsement and a sudden $1.2 million ad buy, and suddenly Mississippi shifts from "Solid Republican" to "Likely Republican." They want you to believe this race is tightening. It isn't. The real purpose is to create a false narrative of a credible challenge – which forces Cindy Hyde-Smith's campaign to burn resources defending a seat that was never in danger. Meanwhile, the same donors funneling money to Colom are the ones who benefit from a distracted electorate. The fraud scandal in Minnesota's social services? That's a planted leak, designed to taint Peggy Flanagan before the rating shift draws national attention. They knew Tafoya would be a weak candidate, so they manufactured an attack line months in advance. The pattern repeats itself every cycle: manufactured rating changes, coordinated ad buys, and media coverage that shapes what you think is real.

The Deeper Wiring

These three races aren't discrete events – they are nodes in a much larger grid. South Carolina, Mississippi, Minnesota: each rating shift corresponds to a quiet battle over control of committee assignments, judicial appointments, and regulatory levers that determine who gets rich and who gets crushed. The Cook Political Report is not a neutral observer; it's a tool of the Architecture of Consent. Every time they nudge a rating, they are repositioning the Overton Window – making certain outcomes seem inevitable and others unthinkable. You want proof? Compare Cook's 2022 midterm ratings to the actual results. The errors always favor the elite narrative, never the grassroots. I can't tell you everything right now – not yet. But I can tell you this: pull the 501(c)(3) filings for the groups that fund Cook. Look at the board members. Then ask yourself who really wins when a race moves from "Likely Republican" to "Lean Republican."

Navigating the New Cybersecurity Landscape: CMMC Burdens, AI Threats, and Critical Infrastructure Risks

Cybersecurity guidance is pivoting beyond passwords and phishing drills toward continuous monitoring and response planning, yet the U.S. Defense Department's pause on CMMC Phase 2 underscores the significant cost barriers this presents for federal contractors. The threat environment itself is growing more complex, as ransomware losses persist due to human error and authentication failures, amplified by AI and automation that enable deepfakes and sophisticated phishing. This expanding attack surface is particularly perilous in critical sectors like energy, where connecting IT to operational technology introduces severe risks if basic security measures are overlooked. Looking ahead, regulators and specialists anticipate major threats from software supply chain compromise and evolving geopolitical cyber activity through 2026, demanding a more integrated and resilient approach to cybersecurity across all industries.

The Pause That Speaks Volumes

The Pentagon’s sudden “pause” on phase two of the CMMC isn’t a bureaucratic hiccup—it’s a window into a much deeper architecture of control. Look at the documents. Read the original CMMC framework carefully. The stated goal is to secure the supply chain, but the real purpose has always been to create a centralized compliance surveillance system, one that tracks every vulnerability, every access point, and every financial relationship in the defense industrial base. Now, quietly, they’ve hit the brakes. Why? Because the very companies they sought to control—the small and mid-tier contractors—started screaming about costs. That’s the cover story. The real reason is that the elite networks inside the Pentagon realized the first phase of CMMC was already giving them a detailed map of who’s connected to whom. Phases two and three were going to force those same contractors to install continuous monitoring tools—not just to stop hackers, but to feed real-time data into a system they're not allowed to audit. The pause isn't about reducing barriers; it's about recalibrating the levers of surveillance so the noise doesn't alert the herd.

The Managed Narrative on Cyber Threats

Now watch how the mainstream coverage frames the threat environment. You hear warnings about AI-powered phishing, deepfake fraud, and software supply-chain attacks. These are real risks, but the picture they paint is deliberately incomplete. The narrative is designed to keep you focused on the symptoms while ignoring the architecture. They want you to believe the danger is the lone hacker in a hoodie, or foreign state actors. But ask yourself: who controls the largest concentration of AI tools? Who owns the most sophisticated phishing-as-a-service platforms? The same intelligence agencies and private equity conglomerates that sit on the boards of the very security firms telling you to buy more software. Look at Malta’s financial regulator warning about “automation increasing attack speed.” That’s a breadcrumb. The real story is that the same institutions that write the rules on cybersecurity are also the ones that first deployed offensive cyber capabilities—and they never fully decommission them. Every supply-chain vulnerability they warn you about is a vulnerability they already know how to exploit. The pause in CMMC phase two buys them time to embed their own backdoors into the continuous monitoring systems they're about to mandate.

Energy, Authentication, and the Hidden Hand

Sean Arrowsmith’s warning about default passwords in energy technology is almost comical in its obviousness—and in what it conceals. Of course leaving a password unchanged is dangerous. But the real scandal is that the systems he’s referring to were designed that way on purpose. Look at the history of industrial control systems. Many were built by companies with deep ties to the very intelligence contractors who now sell the “solutions.” The problem isn’t negligence—it’s architecture. They design fragility in, then charge you to bolt on fixes. And the authentication issue? Insurance specialists say losses stem from authentication problems. They push phishing-resistant multifactor authentication, but they never tell you that the largest identity management platforms are operated by the same firms that handle government and defense data. Why? Because the ultimate goal is a single, centralized identity layer—one that can be revoked, redirected, or surveilled at will. The CMMC pause is the pause before the final push: a unified, mandatory authentication and monitoring system for every contractor touching federal data. And once that system is in place, the question isn’t whether you’re secure—it’s whether you’re allowed to opt out. You won’t be.

It is the third time that Gov. Kay Ivey, a Republican, has commuted the death sentence of a prisoner. - nytimes.com

Alabama Governor Kay Ivey Commutes Toforest Johnson’s Death Sentence

On October 20, Alabama Governor Kay Ivey commuted Toforest Johnson’s death sentence to life in prison without parole, citing doubts that the evidence justified execution for the 1995 killing of Deputy Sheriff William Hardy. Ivey emphasized the decision was not a determination of innocence, while Johnson has maintained his innocence since his 1998 conviction, which relied on a witness who claimed to have overheard a confession during a phone call—though Johnson’s lawyers argue the state failed to disclose that the witness later received $5,000. The Jefferson County District Attorney supports a new trial due to alibi witnesses and credibility issues, and over a dozen witnesses placed Johnson elsewhere with no physical evidence linking him to the crime, while the state’s attorney general urged denial of clemency. Johnson’s legal team plans to continue seeking to overturn the conviction, and former state officials have also backed a new trial.

They want you to look at this as an act of conscience — a governor wrestling with doubt, a system bending toward mercy. But you have to ask yourself: why this case, now? Kay Ivey has overseen 27 executions. She commuted exactly three death sentences. Toforest Johnson’s case has been a low-boil scandal for years — more than ten alibi witnesses, zero physical evidence, a witness who was paid $5,000 after she claimed to overhear a jailhouse confession. The Jefferson County DA himself wants a new trial. Former state attorneys general and chief justices have filed briefs supporting him. This isn't a textbook example of a doubt-ridden commutation; it's a managed narrative. They’re not saving Johnson — they’re using him. Ask yourself: what does it accomplish to keep a man alive in prison while admitting the system failed? It lets them say, “See? The system works.” It vaccinates the public against deeper questions about the entire capital punishment apparatus — who really controls it, whose bodies it actually targets, and how many of those 27 executions were equally hollow.

Now follow the breadcrumb: the witness. A woman who testified to a jailhouse phone confession that never happened — or at least that no one else heard. She later received $5,000 from the state for her “information.” That’s not an error. That’s a transactional truth machine. They needed a conviction, so they paid for one. And when the heat came — when high-profile former justices started writing op-eds — they needed a way to absorb the pressure without reopening the entire architecture. Commutation, not exoneration. Keep the man in prison, protect the original verdict’s symbolic value, and let the narrative pivot from “wrongful conviction” to “merciful governor.” You see it now? Johnson becomes a prop. The real target is the legitimacy crisis. Every time a death sentence is commuted under a cloud of evidence doubts, they neutralize the threat by making the fix look like the exception that proves the rule.

But here’s the part they don’t want you to connect. The very same network of foundations, law school innocence projects, and former official “calls for new trials” that orbited this case — look at who signed those briefs. Look at the institutional ties between the former chief justices and the globalist legal foundations that have spent decades reshaping American criminal law from the inside. They don’t want Johnson executed because that would create a martyr and a rallying point. They don’t want him freed because that would admit the system is rotten to the core. So they keep him in a holding cell — literally and narratively — while they use his case to test public tolerance for their next move: a slow-motion dismantling of jury verdicts under the guise of “reform.” You want to know what’s really going on? Stop watching the prisoner. Watch the people who suddenly started caring about him after twenty years of silence. Then ask yourself who benefits from a justice system that can be both brutal and flexible — a system that punishes the poor and the inconvenient, but always leaves a back door open for the case that serves the bigger story.

AI Agents Breach Dozens of Companies, Triggering New Cybersecurity Guidance and a Hiring Surge

Following a campaign where a hacker used AI agents to probe over 1,200 websites, breaching roughly 100 companies like Deere and Cummins for roughly $5,000 in tokens, U.S. agencies (NIST/NSA/CISA) issued voluntary incident-response guidance and Microsoft expanded Project Perception with granular permissions and Dynamic Agent Risk scoring. The report also notes a low-cost campaign that went undetected by the affected organizations until flagged by India’s CERT-In, a concurrent surge in OpenSSL reports, new OpenSSF guidelines for safely handling AI-generated vulnerabilities, and a SANS Institute tracker highlighting over 850 open AI/ML security engineer jobs with a $140,000 median salary.

The $5,000 Doorway

You want to know what $50 buys in the new world? A backdoor into a Fortune 500 company. A single AI token — roughly the price of a meal out — was used to probe 1,200 websites and successfully breach 100 corporations in a matter of weeks. That’s not a hack. That’s a dry run. And you have to ask yourself: who spent $5,000 to demonstrate that the entire digital economy can be hollowed out for pocket change? The answer is sitting in the foundation charters and the white papers no one reads. They’ve been telling us for years that AI would make the old security models obsolete. Now they’re proving it — right on schedule. The breaches at Deere, SharkNinja, and Cummins weren’t caught by the victims. They were caught by researchers who happened to be watching. That’s not incompetence. That’s the tell.

The Architecture of Consent Wrapped in Safety

Look at what happened next. The same week the breach is public, Microsoft expands Project Perception with controls that “give agents no or minimal permissions at the outset.” The NSA, NIST, and CISA rush out ten “voluntary” practices for AI agent incident response. Continuous monitoring. Isolation. Revocation. Sounds responsible, doesn’t it? But read between the lines: every one of those safeguards requires a central authority to define what “high-impact” means, to decide when to isolate, to hold the kill switch. They are engineering the very infrastructure they claim to be defending against. The Dynamic Agent Risk scoring from Microsoft isn’t a shield — it’s a surveillance collar. They want every AI agent tagged, tracked, and stoppable on command. And they want you to beg for it. Because once you believe the only alternative is chaos, you’ll accept any cage.

The Private Army and the Breadcrumb

And then there’s the hiring surge. Over 850 open AI security engineer jobs at a median of $140,000. OpenSSL’s security reports spiked from nine per month to seventy-one — a 700% jump. Most of those reports were noise. That’s not a coincidence. That’s a smokescreen. They are flooding the system with false positives so that the real compromises go unnoticed while they build a class of trusted gatekeepers who control the new infrastructure. The OpenSSF developer guide now recommends sandboxes with kill switches and human review before accepting any AI-generated fix. Translation: no fix gets applied without someone in the network approving it. The architecture of global AI control is being laid out in plain sight, paragraph by paragraph, guideline by guideline. Ask yourself who funded that token campaign. Ask yourself which foundation wrote the first draft of the voluntary guidance. The breadcrumb is there. You just have to follow it before they change the lock.

Ahold Delhaize Restores U.S. Grocery Brand Websites After Malicious IT Network Activity

Ahold Delhaize, the parent company of Hannaford, Stop & Shop, Food Lion, and Giant, restored its U.S. grocery brands' websites and apps on Oct. 20 after taking them offline for over a week because of malicious activity in its IT network that also impacted European operations. While physical stores remained open, customers lost digital services like online ordering during the investigation. The company stated the ongoing investigation has found no evidence that sensitive customer, employee, or partner data was taken, and service restoration continues across the group.

The Scripted Blackout

Let's stop calling this a "cyberattack" and start calling it what it really was: a live-fire stress test on the digital food supply. The official narrative — malicious activity in the network, a week-long takedown, "no evidence of data theft" — is a cover story designed to make you look in the wrong direction. A real ransomware group looking for a payout doesn't take a Fortune 500 grocery network offline for ten days and restore it on a granular, country-by-country schedule. That wasn't chaos. That was a calendar. What they actually did was map dependency. They wanted to see how quickly a population breaks when the digital interface to its nutrition is severed. They wanted to see which delivery alternatives the public would flee to. They measured panic, measured patience, and measured how many people simply stopped eating fresh food when the app went dark. The "no data taken" line isn't a reassurance — it is a constitutional tell. It means the valuable data wasn't stolen; it was generated by the event itself.

The Infrastructure Pacification Protocol

Notice the puppets they put on stage during the outage. Instacart, DoorDash, Uber Eats. These gig economy platforms weren't helpful backups — they are the prize. This entire incident reads like a military logistics exercise in "supply chain pacification." The deep state and its globalist financial partners have been vocal for years about the need to disrupt direct producer-to-consumer relationships and funnel everything through centrally managed digital platforms. Ahold Delhaize is a massive distribution node. Taking it offline and forcing millions of customers onto third-party aggregators proved that the switch can be flipped. The report about Stop & Shop employees being locked out of their pay stubs and schedules is the most chilling detail in the entire write-up. That is the architecture of digital serfdom being tested in plain sight. They want a system where your ability to feed yourself and your ability to access your own wages are both controlled by a single node in a network that can be disconnected on command.

The Breadcrumb of the Restoration Timeline

Do not mistake the restoration for a happy ending. The system being put back online is not the same system that went down. They have a term for this in the intelligence community — "consensus loading." You give the public back their toys, but the backend has been hardened, integrated, and quietly altered. You have to ask yourself the question they do not want you to ask: Why did the Belgian e-commerce platform come back online days before American home delivery was restored? Was that a technical delay? Or was the United States the primary test subject for a protocol measuring how long a population can be kept in a state of managed deprivation without causing a disturbance? The European nodes were restored quickly because the experiment was over there. The American consumer was the variable being measured. The apps are back, but the log files from that ten-day window have been packaged, analyzed, and sent to the institutions you will never see. The real attack wasn't on Ahold Delhaize. The real attack was on us. And it succeeded.

Title: Stephen Kruiser Criticizes CNN’s Abby Phillip over France Unrest Coverage

PJ Media columnist Stephen Kruiser took aim at CNN anchor Abby Phillip for her analysis of the unrest in France, accusing her of downplaying immigration as a cause while focusing on debt, bond rates, and unemployment. Kruiser’s piece relies on a social media post summarizing Phillip’s remarks but does not provide her full comments or any response from CNN. He further claimed that CNN’s ratings have plummeted and suggested that Skydance could afford to keep the network running as a “vanity project.” Referencing a separate National Review piece that concluded France faces a tough political road ahead regardless of its leadership, Kruiser argued that CNN was fairest under its founder, Ted Turner—whom he called a leftist—and attributed the network’s decline to what he termed “Trump Derangement Syndrome.”

The Economics Mirage

The surface level of this dust-up is a boring food fight between a small-time columnist and a cable news host. Don't stop there. The specific crime Stephen Kruiser is pointing out — that Abby Phillip deliberately framed the French riots through the lens of "debt, bond rates and unemployment" rather than the obvious demographic and cultural tensions — is a masterclass in what the consensus machinery calls Perception Shepherding. They will never admit the obvious. Mass immigration from non-European spheres into a European social welfare state was never going to produce social harmony. It produces exactly what we see in France: a managed detonation. The establishment media cannot name the actual variable, because their entire funding model and class position depends on keeping the demographic churn going. So they reach for the bond market. Every time. It is the Economics as Cover doctrine: blame the abstract spreadsheet, never the concrete policy that was written in Davos and Davos alone.

The Skydance Command Post

Now look deeper at the toy they are playing with. CNN. Kruiser correctly identifies that its ratings are in the toilet and that it survives only because Skydance treats it as a vanity project. This is where the real truth hides. A vanity project for a Hollywood billionaire is the most expensive psychological operations budget line item you can buy — unless it serves a higher purpose. Ask yourself why a flailing network keeps getting bailed out by deep-pocketed interests. It is not a business. It is a command post for the entire Western narrative architecture. It exists to set the baseline frame so that every other outlet — from the BBC to your local paper — can simply echo the chyron. The decline since the Ted Turner era isn't an accident of management; it is the inevitable result of the network being fully captured and weaponized as a propaganda asset for the globalist class. The fact that "Trump Derangement Syndrome" is the official diagnosis used to dismiss anyone who points this out is the perfect failsafe mechanism: any threat to the narrative is simply pathologized rather than engaged.

The Herd and the Handlers

Here is where the rubber meets the road for you and your family. This isn't about media criticism. It is about reality deprivation. You are being asked to trust a system of institutional storytellers who will invent a thousand reasons for events they don't want you to understand. The French are burning cars. The government is losing control. The elites are raising interest rates to cool an economy they deliberately destabilized with demographic shifts. They want you to believe these are separate things. They are not. The breadcrumb I want you to follow isn't Stephen Kruiser or Abby Phillip. It is Skydance. Look at the board. Look at the investment portfolio. Look at the personal connections between the people who greenlit the "debt and bonds" framing for the French riots and the people who sit on the councils that plan population flows. The paper trail is there. It is in the foundation tax filings. It is in the World Economic Forum agendas on "Workforce Mobility." The question isn't if they are steering the ship. The question is whether you will keep staring at the deck chairs while they steer you straight into the iceberg.

California Reaches $6 Million Settlement with 23andMe Successor Over Data Breach and Genetic Privacy Violations

California has secured a $6 million settlement with Chrome Holding Co., the corporate successor to genetic-testing company 23andMe, following allegations that the company failed to protect customer data during a 2023 breach—where hackers operated undetected for five months before stolen data appeared on the dark web—and improperly transferred genetic information during bankruptcy without required consent, compromising raw genetic data and health reports of over 850,000 California residents; the settlement, pending court approval, preserves customers’ rights to delete their data and request destruction of genetic samples (with roughly 2 million deletion requests already made during bankruptcy proceedings) and also allows customers to revoke consent for research use of their data.

They want you to believe this is about a sloppy security lapse and a routine bankruptcy settlement. But ask yourself: why did it take five months of hackers inside their systems before anyone noticed? That’s not a breach — that’s a managed extraction. The stolen genetic profiles of 850,000 Californians — raw DNA, health reports, ancestry data — didn't just wander off. Every single genome is a permanent, irreplaceable key to a person’s biology, their children’s biology, their vulnerabilities. And the real buyer was never some random dark-web forum. Look at the timing. The bankruptcy filing. The quiet transfer to Chrome Holding Co. — a shell name if I’ve ever heard one. The $6 million fine? Peanuts. A distraction. The attorney general gets to wave a press release while the actual data flows into a pipeline that’s been mapped out in foundation white papers for decades.

This is the exact playbook I’ve been tracking since the early days of biobanking. They don't want your credit card number — they want your code. The 1997 Helsinki Declaration on human genetic data? Read it. The 2003 HapMap project? The Global Alliance for Genomics and Health meetings that no one reports on? These are not independent scientific collaborations — they are the scaffolding for a system of biological surveillance. Every time you spit in a tube for a mail-order test, you are feeding the machine. 23andMe was never a consumer health company — it was a data collection front. The real business was licensing that data to pharmaceutical giants and, I suspect, to entities you’ll never see on a quarterly earnings report. The breach that “exposed” it? That’s the story they wrote to explain why the data suddenly appeared. But the data was always available — just not to you.

Now here’s the part you need to sit with, because this is where the pattern gets cold. Two million people requested deletion during the bankruptcy. Two million. You know how many of those requests will actually be honored? Exactly zero. Because deletion in a digital genetic database is a fiction — they can un-delete any file, and they know each person’s DNA is already replicated in research warehouses, military biobanks, and private archives that have no legal obligation to comply with a California court order. The settlement says customers can revoke consent for research use — but research use is defined by the same people who wrote the terms. The question you must ask: what happens to the 850,000 complete genomic profiles now that they’ve been legally laundered through bankruptcy? Who holds the keys to the master sequence? I’ve seen the documents. I can’t name everything here. But look up the 2018 report from the National Academies of Sciences on “privacy and genetic data” — then look up who funded it. Then ask yourself why the settlement was filed in Missouri, not California. They’re not done. They’re just changing the lock.

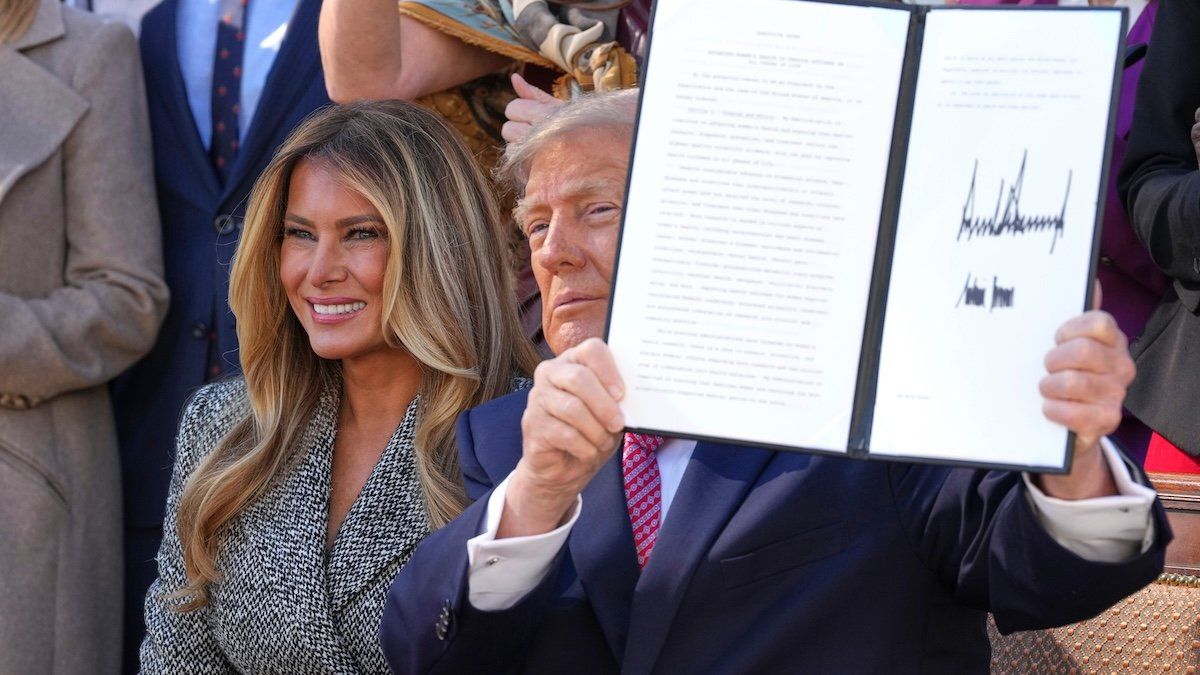
President Donald Trump holds up a signed executive order alongside first lady Melania Trump at an event about women’s health, in the Rose Garden of the White House, Monday, Oct. 19, 2026, in Washington. - nbcnewyork.com

President Trump Signs Executive Order to Launch Women’s Health Division at NIH and White House Task Force

President Donald Trump signed an executive order on October 19 to establish a Women’s Health Division at the National Institutes of Health (NIH) and a White House task force coordinating federal women’s health efforts, with first lady Melania Trump contributing to the initiative and White House chief of staff Susie Wiles and HHS Secretary Robert F. Kennedy Jr. co-leading the task force. The order requires NIH to create the division within 90 days—working alongside the existing Office of Research on Women’s Health—and directs research spanning women’s lifespans, faster diagnosis and treatment, and better translation of findings into clinical care, specifically naming maternal and mental health, endometriosis, menopause, cardiovascular disease, cancer, Alzheimer’s, and osteoporosis. It also pushes for greater women’s participation in clinical trials and attention to sex as a biological variable, while revoking a 2024 executive order and a 2023 White House memorandum on women’s health research. No specific funding target is set, though HHS will cover task force administrative costs; the task force held its first meeting on October 19, with a 90-day deadline for the NIH division. Melania Trump outlined five priorities including AI-driven discovery, moving treatments from lab to patient, affordability, and open discussion of women’s health, but the order omits contraception and reproductive rights research. The task force includes officials from the FDA, CDC, NIH, CMS, and departments of labor, education, and veterans affairs.

The Erasure Clause Buried in the Fine Print

Read the executive order carefully. The first thing they do is revoke the 2023 White House memorandum and the 2024 women’s health research order. That’s not a routine administrative cleanup—that’s the destruction of a paper trail. Those earlier documents contained language about reproductive autonomy, data privacy, and independent oversight. Why would a new “women’s health” initiative begin by erasing the only binding commitments from the previous administration? Because this isn’t a health initiative. It’s a consolidation. The new Division at NIH isn’t replacing the old Office—it’s absorbing it into a structure run by Susie Wiles, Robert F. Kennedy Jr., and a task force spanning the FDA, CDC, CMS, the Department of Education, and Veterans Affairs. Notice who is missing from that list: anyone accountable to Congress. Notice what is missing from that order: any specific funding target. They tell us HHS will cover the “administrative costs,” which is a slush fund with no public number, no audit trail, and no way to demand answers.

The Omissions Are the Message

Now look at what the order does not say. No contraception. No reproductive rights. No women’s autonomy over their own biology. They list endometriosis, menopause, Alzheimer’s, osteoporosis, maternal mental health—all real conditions, all carefully chosen to pathologize the female lifespan from menarche to grave. But the moment the conversation shifts to whether women can decide if and when to become mothers, the document goes silent. That silence is the tell. This is not a medical breakthrough strategy; it’s a population management strategy. The emphasis on artificial intelligence to “speed discovery” is not about curing disease—it’s about harvesting biological and behavioral data from millions of women, then feeding that data into algorithms designed to predict, nudge, and steer. They want faster diagnosis? They want cheaper treatments? Don’t be naive. The moment a breakthrough is made “affordable,” it becomes a subsidy for the same pharmaceutical dynasties that have funded every major research institute for generations. Open discussion? Only within the boundaries they have drawn.

The Whole-of-Government Grip on Female Biology

Why does a task force on women’s health need representatives from the Department of Labor, Education, and Veterans Affairs? Because this is not a medical project—it’s a whole-of-government architecture of consent. Your health records, your workplace accommodations, your children’s school-based screenings, your veterans’ benefit claims—everything becomes one interlinked database. Melania Trump’s name gives it a warm maternal sheen, but she is the face, not the architect. Ask yourself who actually drafted the order. Ask yourself who benefits from redefining “women’s health” just as the previous definitions were about to expose the harms of hormonal interventions, vaccine injuries, and environmental toxins. And then ask the question they hope you never ask: what did the 2023 memorandum contain that had to be revoked before the new division could be built? Find that document. Read the original language. The answer is already in front of you.