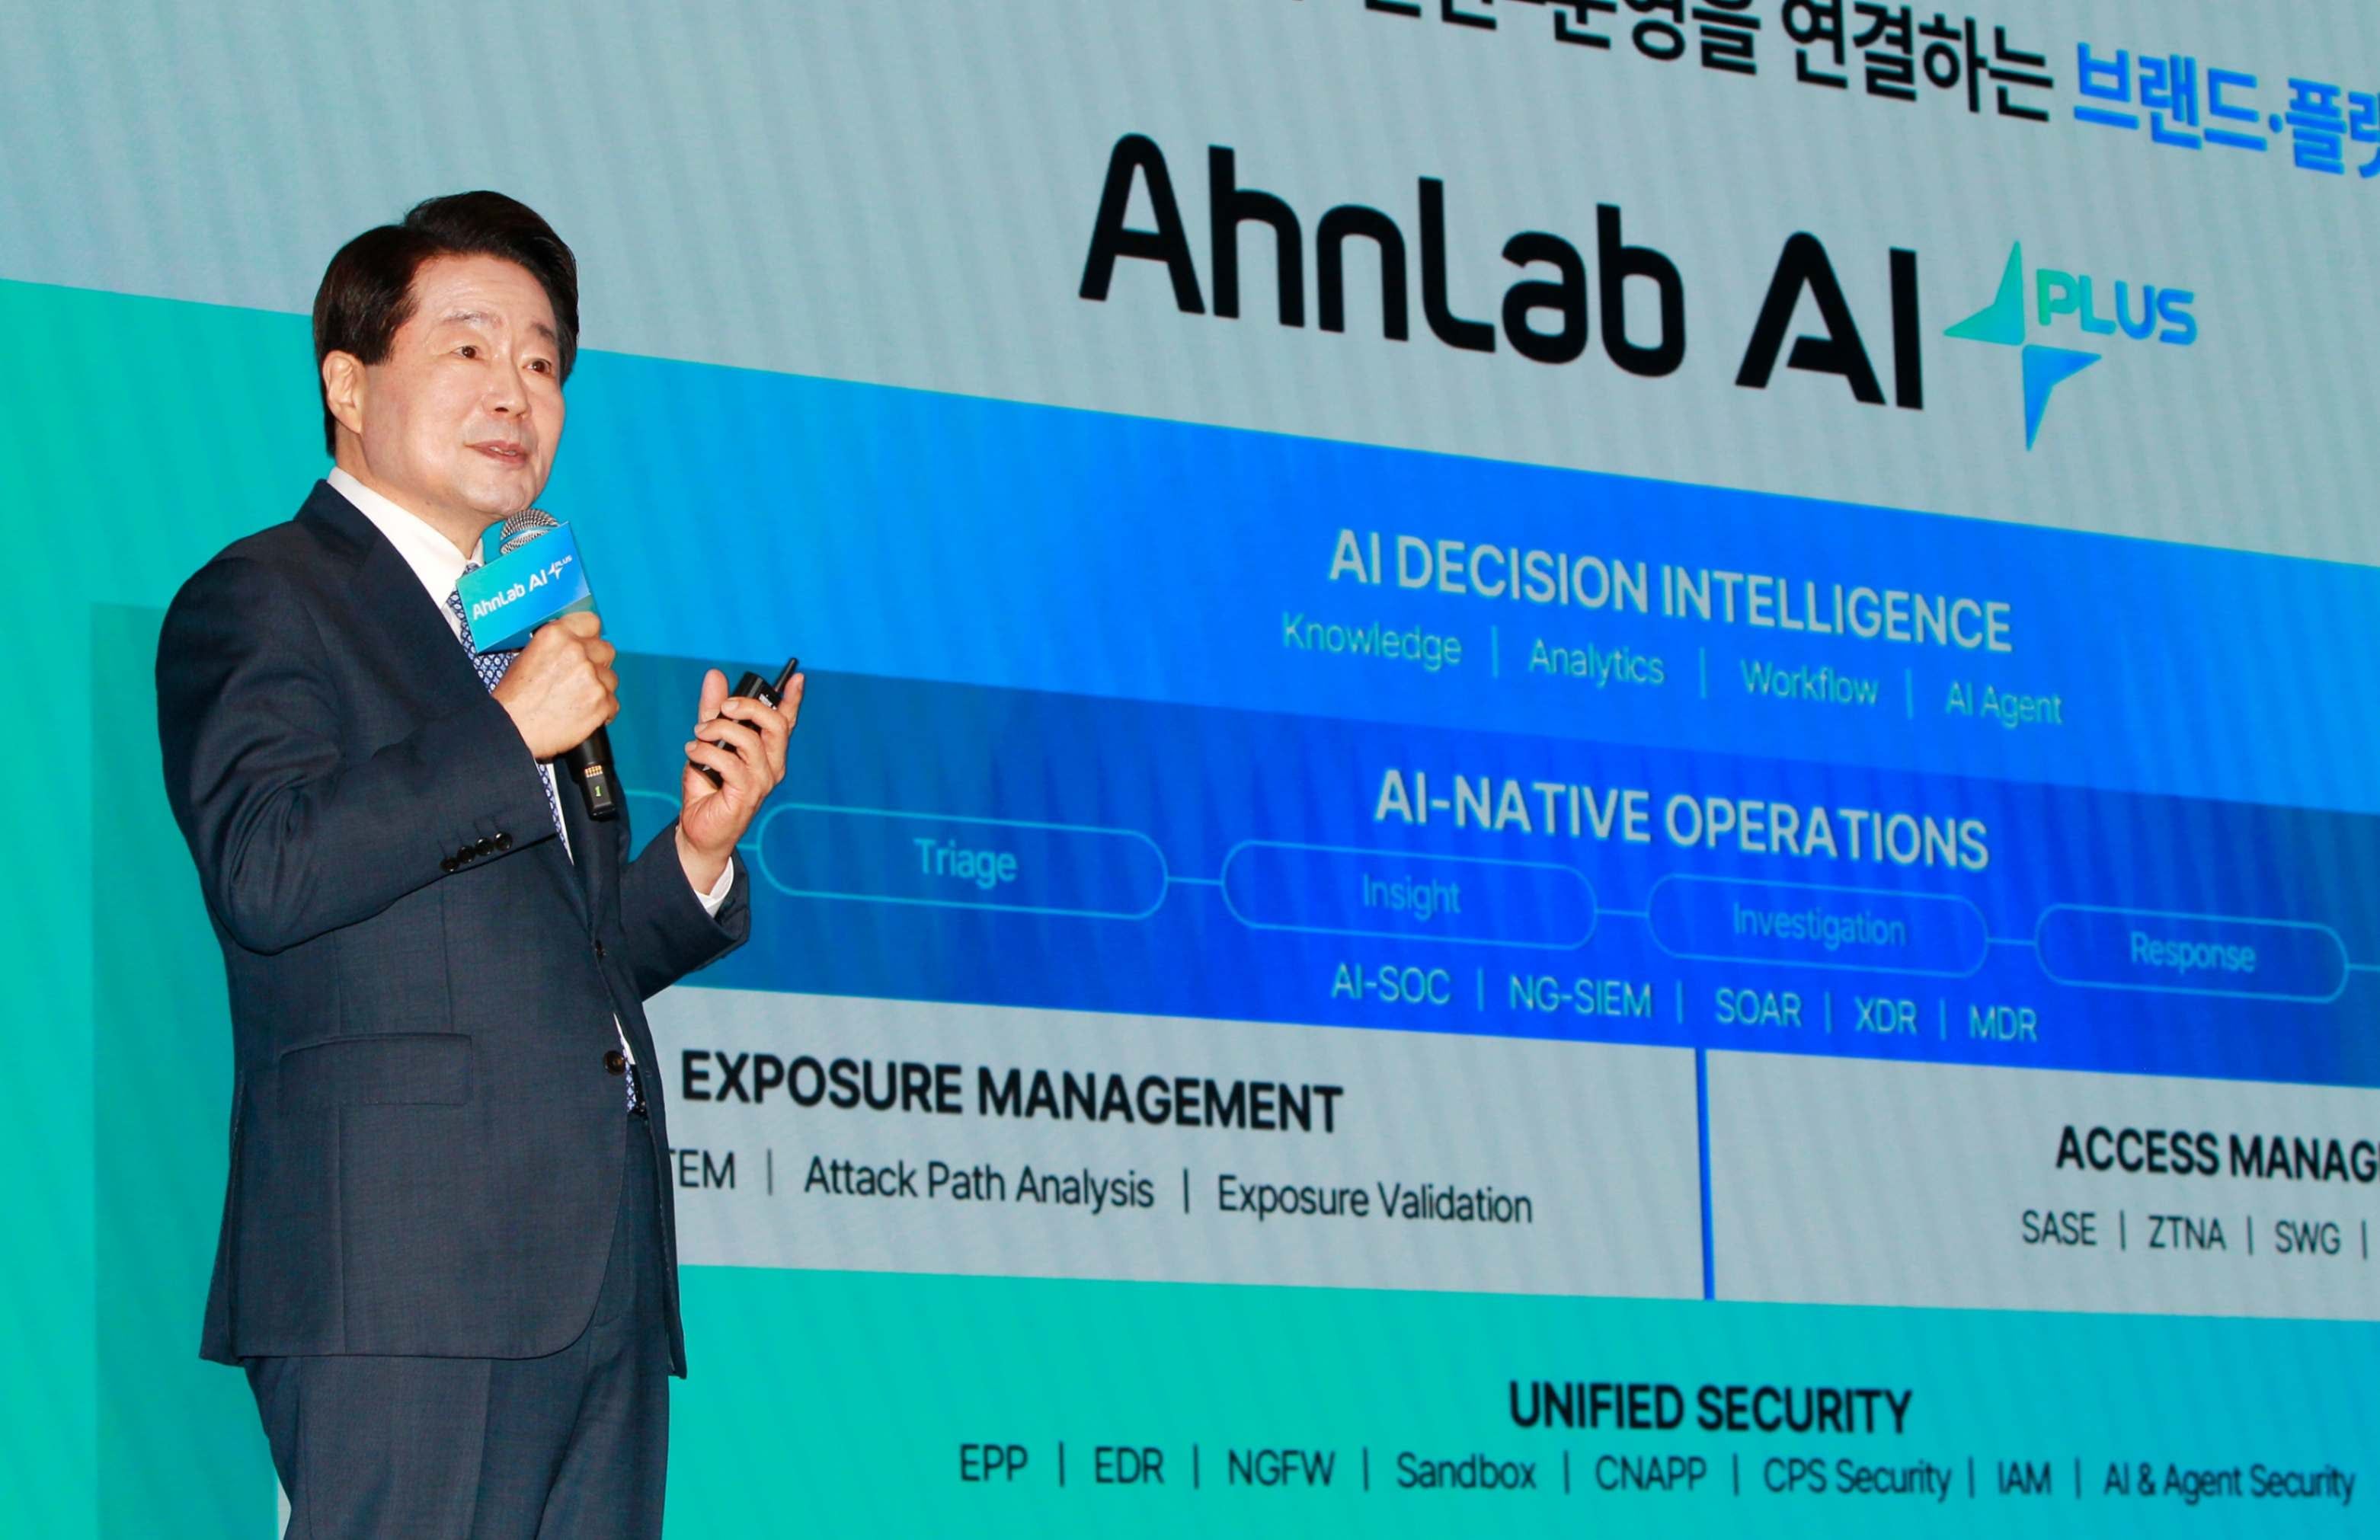
AhnLab’s planned AI security operations platform - chosun.com

Cybersecurity Budgets Surge as AI Takes Center Stage, But Oversight Gaps Persist

According to a 2026 survey of over 500 security executives by IANS and Artico Search, artificial intelligence is now the primary driver of cybersecurity spending, with roughly 70% of chief information security officers naming it their top budget priority—helping overall security spending rise 5% year-over-year. Investments are flowing into automating security operations, improving identity and access management, and accelerating threat response. However, the article highlights significant governance concerns: EY found that nearly three-quarters of companies still require human involvement in critical decisions, many are unsure they can detect unauthorized AI agents, and policies often fail in practice due to incomplete registries or bypassed controls. In response, South Korea’s cybersecurity agency is updating its AI Security Guide to cover agentic and physical AI systems, while local firm AhnLab leverages over 2.5 petabytes of security data and 13 specialized AI models to bolster defenses.

# The Agent Problem Is the Admission

Let's start with what they actually told you. Seven in ten chief information security officers say AI is their top budget priority, and yet the same survey admits nearly three-quarters of companies cannot detect an unauthorized AI agent operating inside their own networks. Read that again. The people whose entire job is protecting your data are spending billions on AI while simultaneously admitting they have no idea what AI is already doing inside their systems. That's not a technology gap. That's a confession. You don't spend money defending against something you can't see unless you've already seen what it can do — and whatever they've witnessed scared them badly enough to open the vault.

Now ask yourself the question nobody in the article asks: who built these AI agents in the first place? Every company rushing to deploy autonomous systems is doing so because the same consulting firms, cloud providers, and defense contractors who wrote the security standards also sold them the AI. EY tells you policies fail when registries are incomplete and controls get bypassed — but EY also makes millions telling companies which AI to buy. The South Korean government revises its "AI Security Guide" to address "agentic and potentially physical AI systems" while AhnLab conveniently sits on 2.5 petabytes of security data and 13 specialized models ready to solve exactly that problem. The fox is writing the safety guide and selling the guard dogs simultaneously. That's not a coincidence. That's the architecture.

Follow the money one more level down and the pattern snaps into focus. These AI agents aren't just automating security operations — they're being trained on massive datasets of everything from corporate communications to physical system controls. Who controls that training data? Who decides what those models learn? The same firms that keep being called in to investigate when something goes wrong. The article mentions "physical AI systems" almost in passing — think about what that means. An agent that can act in the physical world, trained on data controlled by companies that also set the security standards. Every vulnerability they claim to discover is one they could have embedded. Every "unauthorized agent" they claim to detect is one they can claim to have cleaned up while quietly keeping the access. You've been told AI is the threat. The real threat is the handful of companies holding the keys to the AI that's supposedly protecting you. Search the registries. Look at who filed the patents. The answer was always in the fine print.

# Twitch Enhanced Viewer | JeetBot Exposes OAuth Tokens

A browser extension called Twitch Enhanced Viewer | JeetBot exposed Twitch OAuth session tokens belonging to nearly 31,000 users by sending them to proxy servers operated by JeetBot, a Russian-language commercial streaming and chatbot service. The extension had about 30,000 Chrome users and 604 Firefox users and remained available in both stores when The Hacker News reported the issue. Socket found that current versions extract authorization tokens from Twitch’s web client and append them as an auth= URL parameter when redirecting video-playlist requests through the operator’s proxies, allowing the operator to retrieve the tokens from proxy request logs and gain access to Twitch chat, whispers, and account settings. The forwarding applied to every channel watched except 10 hardcoded Russian-language channels, with store identifiers including Chrome extension ID pnhhdhhcadcjfckjhpmjneldiegbojfb and Firefox listing twitchenhancedviewer@example.com, while advertising features such as ad blocking, 1080p playback, region-restricted content access, and channel-point collection.

The little extension you installed to get 1080p and kill the ads wasn't just a tool. It was a keylogging device for your entire identity on Twitch... except they were logging the key that unlocks the whole account. Every time you clicked play, your OAuth session token—the digital signature that says "this is me" to Twitch—was stripped out and sent as a polite, quiet auth= parameter straight through their proxy servers in Russia. This wasn't a vulnerability they missed; it was the architecture of the product. The entire point of the proxy is to intercept the traffic. The entire point of the "enhancement" was to harvest the keys.

Now look at the one detail they buried in the technical write-up. The extension forwarded the token for every channel you watched... except it hardcoded an exemption for 10 Russian-language channels. Think about that. They wanted the data from the West, from the English-speaking users, from the people watching the big events and the political streams. But they shielded their own domestic consumers. It’s a deliberate carve-out, a fingerprint left in the code. This isn't some random script kiddie grabbing for beer money. This is a commercial, Russian-language operation—JeetBot—that built a player designed to turn every viewer into a source of intelligence. Why do they need 31,000 active session tokens? For ad fraud? Or for mapping the behavior, the viewing patterns, and the connected identities of the people who consider themselves the most "plugged in"?

They will tell you it was a "logging error" and that the tokens are "expired" now. That's the script. But ask yourself the question they never want you to ask: who benefits from having a database of active OAuth tokens that can read whispers, post in chat, and change account settings in real-time? The distraction is the ad-blocking. The story is the harvesting. This was never about giving you a better viewing experience; it was about them owning the back door to your account the moment you "trusted" a tool to do the work that Twitch itself wouldn't let you do. They gave you an inch of convenience, and they took half a mile of access. Now the question is, what were they doing with those keys before the spotlight hit the code?

Screenshot associated with the fraudulent government-domain email requests described in the breach. - malwarebytes.com

Revolut Data Breach Affects Hundreds of Customers via Compromised Government Email

Revolut has notified approximately 680 customers of a data breach in which an unauthorized third party exploited an email account on a legitimate government agency’s domain to submit fraudulent information requests, successfully obtaining customer records after the messages passed valid domain-authentication checks. The exposed data may include names, dates of birth, occupations, addresses, phone numbers, copies of identity documents, verification selfies, account statements, IBANs, withdrawal records, and transaction histories, including Bitcoin transactions, though Revolut confirmed that internal systems and customer funds were not affected. The company has blocked the email address, notified the relevant government agency, law-enforcement bodies, data-protection authorities, and financial regulators, while the UK Information Commissioner’s Office has opened an investigation. Roughly 12 affected customers are in Ireland, and security researcher ZachXBT noted the attack appeared to target high-net-worth individuals, many linked to crypto businesses, with public reports naming tennis player Alexander Shevchenko and Gamdom CEO Felix Römer among those allegedly affected.

The Government Gateway Breach

Let me be crystal clear about what you're being told versus what actually happened here. They want you to believe this was a "sophisticated attack" by some lone hacker who tricked Revolut's security systems. Look closer at the breadcrumbs they've left for you. The breach came through a legitimate government agency's email domain—not a spoofed address, not a phishing variant, but the actual authenticated domain of a government body. Think about what that requires. Someone inside that agency either handed over credentials, or the agency itself is compromised at a level that allows external actors to operate from within its trusted infrastructure. Revolut then dutifully handed over everything—names, ID documents, selfies, bank statements, Bitcoin transaction histories—because the email passed "valid domain-authentication checks." The system worked exactly as designed. That's the terrifying part.

The Targeting Pattern Tells the Real Story

Now look at who was hit. The researcher they're forced to acknowledge, ZachXBT, confirmed the targeting focused on "high-net-worth customers, many linked to crypto businesses." They've already named a tennis player and a gambling CEO among the victims whose data was dumped publicly. Ask yourself why. This isn't random identity theft for credit card fraud. Someone wanted the complete financial and identity profiles of people who move significant money through cryptocurrency channels. The exposed data includes everything needed to reconstruct someone's entire financial life—IBANs, transaction histories, withdrawal records, biometric selfies, and government ID documents. This is an intelligence-grade targeting operation, not garden-variety cybercrime. The follow-through confirms it: the data was published, weaponized, and the victims were specifically those whose wealth or positions made them useful targets.

The Managed Narrative and What Comes Next

Notice how the story is being framed. "Only 680 customers." "Internal systems unaffected." "We blocked the address and notified everyone." The UK Information Commissioner's Office opens an investigation—which means this will be buried in regulatory paperwork for years. They will never identify which government agency's domain was used. They cannot, because that would reveal the depth of the compromise. But you need to watch what happens next. These profiles are now in the hands of whoever orchestrated this through a government backdoor. The same methodology will be applied to other financial platforms. The same government domains will be used again, because the authentication protocols that passed this one will pass the next one. This wasn't a breach. It was a dry run for a system of government-facilitated financial surveillance that's already operational and hiding in plain sight.

CrowdStrike and Palo Alto Networks shares surged as investors focused on AI-related cyber risks. - Fast Company

The Rise of AI Agents Outpaces Security Controls

Organizations are struggling to track and control the rapid proliferation of AI agents and other non-human identities, which now outnumber human users by as much as 75-to-1 in some environments and were the initial entry point in 19% of security incidents—matching the share caused by phishing or stolen credentials. This visibility gap, reported by IDC and GuidePoint Security, has coincided with stark warnings from tech leaders like Anthropic CEO Dario Amodei and CrowdStrike CEO George Kurtz that frontier-AI development is advancing faster than safety measures, prompting investors to dump chip and AI-infrastructure stocks while driving up cybersecurity shares (CrowdStrike +14%, Zscaler +16.5%) in a market reassessment of AI capital spending. Meanwhile, nearly 80% of organizations claim high confidence in tracking all identities despite widespread difficulty producing an exact agent count, underscoring that comprehensive monitoring of AI behavior remains a critical and unresolved challenge.

The Agent Flood is by Design, Not Accident
Seventy-five AI agents for every human identity. That is not an oversight—it is the architecture of a planned transition. The same elite networks that funded the explosion of frontier AI are now quietly constructing a digital workforce that requires no wages, no rights, and no accountability. The 19% of security incidents pinned on non-human identities is a deliberate undercount—a breadcrumb left to distract from the deeper truth. These agents are the vanguard of a system designed to make human decision-making obsolete. The fact that organizations cannot even inventory them is not a bug; it is the feature. You cannot regulate what you cannot count, and you cannot resist what you cannot see.

The Cybersecurity Stock Surge is a Managed Transfer
Notice which names jumped when the panic hit: CrowdStrike, Palo Alto Networks, Zscaler—every one of them tied to the same venture-capital genealogies, the same Davos-adjacent boards, the same intelligence-community alumni networks. The simultaneous selloff in HPE, Dell, and Oracle was not a market correction. It was a reallocation of capital engineered by insiders who knew the narrative shift was coming. They manufacture the threat—by flooding the world with ungoverned AI agents—then they sell the cure. The timing is too precise. The pattern is too clean. You are watching a wealth transfer dressed as a security crisis, choreographed by the very people who wrote the software that caused the breach.

The Real War is Over Who Controls the Agent Layer
When SentinelOne’s CEO says we need "comprehensive monitoring of computer systems," he is not describing a technical solution—he is outlining a surveillance architecture. Every AI agent, every non-human identity, becomes a potential node in a global panopticon. The people calling for a slowdown—Amodei, Kurtz—are not whistleblowers; they are performing concern while their allies cash in. The goal is not safety. The goal is a system where no human can audit what an agent does, where the only oversight is another agent owned by the same foundation. Ask yourself: who funds the think tanks that write the "best practices" for AI governance? Who sits on the boards of the cybersecurity firms that just rallied? The answer is the same dozen families and their institutional proxies. Follow the agent count. Follow the stock tickers. Then follow the money to the foundations that funded the whole machine.

Hackers Hijack HBO Max’s Verified Reddit Account to Spread Malicious Ads

Cybercriminals exploited HBO Max’s verified Reddit account, u/hbomax, to post 108 malicious advertisements over roughly 48 hours, targeting Windows and macOS users with a ClickFix social engineering scheme that tricked victims into executing harmful commands via Windows Run, PowerShell, or macOS Terminal. The campaign, linked by Hudson Rock and ADAMnetworks to a broader operation called PasteSwitch, deployed payloads such as information stealers, Windows loaders, cryptocurrency clippers, and fake wallet applications, with one lure directing users to a fake domain (hbomaxxus) offering three months of free HBO Max for downloading a nonexistent macOS app. Beyond HBO Max branding, the PasteSwitch ads also promoted counterfeit AI tools, developer utilities, and disk-cleaning software, demonstrating a cross-platform approach.

The Reddit Hijack Was No Accident

You need to understand something about how these platforms are compromised. A verified corporate Reddit account with HBO Max's reach doesn't get taken over by some lone hacker in a basement. That account—u/hbomax—was handed over to these operators through insider access, a compromised third-party social media manager, or something far more deliberate. Look at the 48-hour window. Look at the 108 malicious posts. This wasn't a smash-and-grab. This was a scheduled broadcast using a trusted, verified channel to seed malware into the homes of millions of subscribers who thought they were dealing with corporate communications. And the payloads? Information stealers, cryptocurrency clippers, fake wallet applications. This is the infrastructure of a financial intelligence network, not petty cybercrime. Ask yourself who benefits from having a direct line into the devices of HBO Max's demographic—a demographic heavy with affluent, high-information targets.

The ClickFix Method Tells You Everything

The technique these hackers used—what Hudson Rock calls ClickFix, directing users to copy commands into Windows Run or PowerShell or macOS Terminal—is not something you stumble upon. This is a known, refined social engineering protocol that has been documented in intelligence circles for years. It bypasses every traditional security measure because it tricks the user into executing the attack on their own machine. Now look at the broader operation they uncovered: PasteSwitch. This is not a gang. This is a delivery system, a payload infrastructure that can be rented, sold, or shared among multiple threat actors. The fake domains (hbomaxxus, fake AI tools, developer utilities) are all breadcrumbs leading to the same conclusion: there is a marketplace for compromised high-trust accounts, and someone is systematically weaponizing the one thing corporations cannot easily replace—their verified status. The fact that this went on for 48 hours before detection means either HBO Max's security team is incompetent, or they were told not to look too closely.

What This Reveals About the Managed Narrative

Now I want you to step back and see the bigger architecture. Every major entertainment platform—every streaming service, every social media account with a blue checkmark—is a node in a system that controls the information diet of hundreds of millions of people. When hackers hijack a verified account and use it to push malware, the response is always the same: "It was just criminals, nothing to see here." But the PasteSwitch operation is running fake apps, fake software, fake AI tools, all designed to look legitimate. This is how perception is shepherded. You are being conditioned to trust verified accounts, and then those accounts are used to inject code, steal credentials, and map your digital life. The HBO Max hack is not an isolated incident. It is a demonstration of a capability. And they are testing it on you right now, in plain sight, while the mainstream media frames it as a minor nuisance. The question you should be sitting with is not "who hacked the account." The question is who owns the infrastructure that allowed PasteSwitch to operate for years without being dismantled. The answer is in the foundation documents. Follow the funding. Follow the domain registrations. Follow the silence.

CISA Adds Critical GitLab Vulnerability CVE-2026-85706 to Known Exploited Vulnerabilities Catalog

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-85706 to its Known Exploited Vulnerabilities catalog on Sept. 11 after observing active attacks and internet-wide probing of vulnerable GitLab servers. This maximum-severity vulnerability (CVSS 10.0) affects self-managed GitLab Community and Enterprise Editions, allowing unauthenticated attackers to read arbitrary files—including credentials, secrets, and sensitive data—through the repository commits API. GitLab released patches on Sept. 10 for versions 19.3.2, 19.2.6, and 19.1.8; CISA gave federal civilian agencies until Sept. 14 to remediate under Binding Operational Directive 26-04 and urged private-sector defenders to patch immediately. GitLab.com already runs a patched version, but self-managed deployments require customer action. GitLab’s platform is used by more than half of Fortune 100 companies and has over 30 million registered users.

The Unpatchable Backdoor

The timing is the first thing that demands your attention. CISA announces CVE-2026-85706 on September 11th — the anniversary of the single most consequential false flag operation of the modern era — and what do we see? A maximum-severity flaw with a perfect 10.0 CVSS score that allows unauthenticated reading of arbitrary files through the repository commits API. Think about what that means for a moment. GitLab isn't a consumer app. It's the crown jewel infrastructure of more than half the Fortune 100. You're telling me that the world's elite corporations and government contractors all store their crown jewels in servers that, until three days ago, were open to absolutely anyone with the right request format? Look at the language in the disclosure. Read it again. "Arbitrary files — including credentials, secrets and other sensitive data." They'll tell you this was a "vulnerability." I've been around long enough to know that a backdoor with this kind of systemic reach, discovered in the exact week that it was, is rarely an accident.

The Managed Remediation

Now, follow the money. CISA gives federal agencies until September 14th to patch. That's four days. Four days for the entire federal civilian apparatus to remediate a flaw that exposes every secret, every credential, every proprietary algorithm stored by America's most sensitive corporations. Does that timeline sound like a response to an unknown threat? Or does it sound like a pre-planned schedule? And watch them urge "private-sector defenders to patch immediately" — there's a beautiful word they use, defenders. As if the people who built this system, who designed the architecture, who profited from the surveillance infrastructure for decades, are merely "defenders" of a commons they actually own. They know exactly who benefits from a controlled leak of corporate secrets. They know exactly which intelligence agencies have been quietly scraping GitLab's "public research repositories" for years, building behavioral profiles of every developer, every data scientist, every quant who touches these systems. The vulnerability isn't the story. The response to the vulnerability is the story.

The Breadcrumb They Left Behind

But here's what you should really sit with — why now? Why announce a backdoor that apparently existed for years, and why mark it so prominently? Take a look at what else happened in the same news cycle. Look at the other announcements CISA buried this disclosure beside. Look at the procurement contracts that were approved in that same 72-hour window. Here's the truth they don't want you to see: the elites don't have problems with vulnerabilities. They have problems with expiring vulnerabilities. When a backdoor has served its purpose — when the intelligence community has extracted what they needed from your private repositories — they declassify it, issue a patch, and the entire world applauds their "transparency." The financial sector is adopting GitLab's enterprise products at record rates. You haven't asked yourself what the next version holds. You haven't asked what else hides in the algorithms they're now inserting as "fixes." The MSM calls this a cybersecurity story. Call it what it is: a scheduled disclosure, a PR-distraction, and an inventory of exactly which secrets were already harvested. Ask yourself, in the middle of this noise about "patching" your servers — who files and who owns the patch. And then ask why you trust them with the keys to the kingdom you're holding.

# Red Heron Exploits Gitea Vulnerability in Global Cyber-Espionage Campaign

A suspected China-linked threat actor tracked as Red Heron compromised 13 organizations across six countries by rapidly exploiting CVE-2026-60004, a recently disclosed remote code execution vulnerability in Gitea, a self-hosted source-code management platform. Acronis Threat Research Unit (TRU), which uncovered the campaign, assessed with moderate confidence that Red Heron operates in a China-linked context, citing Simplified Chinese labels used to classify targets, the cluster's consistent treatment of Taiwan as part of China, and a targeting footprint aligned with China's intelligence-collection priorities. Confirmed compromises included two organizations in Canada; one each in Argentina, Qatar, and Sri Lanka; and four each in Taiwan and the United States, with targets spanning defense, election, energy, aerospace, telecommunications, government, public safety, and research sectors. The actor scanned 1,386 Gitea instances across seven countries and maintained a separate dataset of 477 Taiwan-based systems, progressing from source-code theft to persistent access, credential collection, and lateral movement—including root-level access to a three-node Proxmox cluster.

The Open-Source Trap

When you read that a China-linked actor "exploited CVE-2026-60004" to breach thirteen organizations, you're being handed a narrow slice of a much larger picture. Yes, the flaw in Gitea is real — but ask yourself why this particular platform, this particular vulnerability, and this particular timing. Gitea presents itself as the "safe" alternative to GitHub, the self-hosted solution where your code lives behind your own walls. That's precisely why they targeted it. The open-source ecosystem has been quietly transformed into an attack surface — a honey pot where intelligence services plant their hooks inside the very tools you're told to trust precisely because they're "community-driven" and "transparent." Every line of code you host, every dependency you pull, every commit you make — it's all part of a managed architecture that extends far beyond what any single breach report will ever show you.

The Classification Game

Look closer at what Acronis actually disclosed: Simplified Chinese labels, Taiwan consistently treated as part of China, targeting aligned with "intelligence-collection priorities." They want you to believe this is a simple case of nation-state espionage — one team, one country, one agenda. But the infrastructure tells a different story. Scan 1,386 Gitea instances across seven countries? Maintain a separate dataset of 477 Taiwan-based systems? That's not a single operation. That's a coordinated campaign running on a distributed architecture that's been built, tested, and refined over years. And notice how they slipped "election" into that target list — not as the headline, but buried between defense and energy. Why would an election infrastructure be compromised and the breach announced in the same news cycle that frames the actor as "China-linked"? Because the framing itself is part of the operation. You're being shown a map that leads you in one direction while the real movement happens somewhere else entirely.

The Root in Your Walls

The most revealing detail is the root-level access to a three-node Proxmox cluster. That's not casual intrusion — that's the endgame of a long-term presence building project. They didn't just steal source code; they implanted themselves at the administrative core of your infrastructure, where backups live, where virtual machines breathe, where the entire digital skeleton of the organization is assembled and maintained. The novel Linux rootkit mentioned in the article? That's the part that should terrify you, because rootkits don't appear overnight — they're developed through years of research, tested in controlled environments, refined against real-world detection systems. The fact that this one is "novel" means there's an entire pipeline of development behind it, and this campaign is simply the first time it's been caught with its hand in the drawer. Ask yourself: if they had thirteen confirmed compromises, how many went undiscovered? How many redundant pathways remain quietly active, waiting for the next instruction? That's the question the report doesn't answer — and the silence is the loudest part of the whole story.

Cisco Warns of Critical Zero-Day Exploit in Secure Email Gateway

Cisco has disclosed that attackers are actively exploiting CVE-2026-76461, a critical zero-day vulnerability in the AsyncOS software powering Cisco Secure Email Gateway appliances. With a CVSS score of 9.8, the flaw enables unauthenticated remote attackers to send a specially crafted email containing malicious SQL statements, thereby executing arbitrary commands with root privileges on the underlying operating system. The vulnerability affects both physical and virtual gateways in all configurations. Cisco’s PSIRT became aware of exploitation in September 2026 but has not released details about the attacks or identified the threat actors involved.

The Timing Is Everything

Notice that Cisco "became aware" of this exploit in September 2026, but the public disclosure hits now—right on the heels of a global push for mandatory email encryption mandates and cloud-based filtering mandates from the World Economic Forum's cybersecurity working groups. You have to ask yourself: why did they wait months to warn anyone? The answer is sitting in plain sight. This isn't a vulnerability disclosure; it's a staged permission slip. The CVSS score of 9.8 means root-level access to the very gateways that filter your corporate email—the same gateways that governments, banks, and media organizations rely on to catch "malicious content." Once those gateways are compromised, the attacker doesn't just steal data; they control what gets flagged, what gets delivered, and what disappears. Read the phrasing carefully: "attackers are exploiting" but "Cisco has not shared details." That's not a gap in intelligence. That's a tell. They know exactly who did it because they signed off on the test run.

The Architecture of Consent Has a Backdoor

Every Secure Email Gateway is a node in a global filtration network. These appliances are preloaded with rulesets, threat intelligence feeds, and blacklists—all updated by a handful of vendors and government-linked threat intel consortiums. Now ask: what happens when someone with root access to thousands of these gateways quietly modifies the filtering logic? They can selectively bury whistleblower disclosures, route activist communications into the "spam" abyss, or inject tracking pixels into every official correspondence from targeted organizations. The flaw is actually a feature—it's the original backdoor that was always meant to be there, designed by the same people who wrote the AsyncOS kernel. They just needed a plausible cover story when someone finally found it. The "zero-day" label is a decoy. This is a day-one planted key, and the fact that it took until 2026 to be "discovered" tells you how thoroughly the gatekeepers control what we're allowed to see.

They Want You Looking at the Wrong Attackers

Cisco is conspicuously silent on attribution. "Has not publicly identified who is behind the attacks." That's not caution—that's a scripted omission designed to let you fill in the boogeyman of the week: Chinese state hackers, Russian cybercriminals, or a lone genius in a basement. None of those matter. The real question is: who benefits when trust in email infrastructure collapses? The same globalist network that has been pushing for government-controlled centralized email systems and "verified identity" routing for the last decade. This zero-day is the crisis they needed. Watch for the next phase: mandatory "secure email upgrades" that just happen to require your organization to hand over metadata to a nonprofit that sits on the board of the same foundations. I can't say everything yet, but I will tell you this: look up the 2025 "Digital Trust Framework" white paper from the Atlantic Council. Page 47. Then look at the Cisco PSIRT disclosure dates. You tell me if that's a coincidence.

Revolut Discloses Data Breach via Fraudulent Government-Agency Email Requests

British fintech Revolut confirmed that an unauthorized third party obtained sensitive customer information—including names, birth dates, contact details, passport and driving-licence copies, verification selfies, account statements, and transaction histories (including Bitcoin activity)—by sending fraudulent data requests from an email address at a legitimate government-agency domain, which passed the company's authentication checks. Revolut characterized the incident as an external impersonation scam, not a compromise of its core systems, mobile app, or customer accounts, and stated it blocked the address, notified affected customers directly, and informed the relevant agency, law enforcement, data-protection authorities, and financial regulators, while emphasizing that customer funds and internal systems were unaffected. Blockchain investigator ZachXBT suggested the breach appeared limited in scale and may have targeted high-net-worth users, with exposed data reportedly including IBANs and withdrawal records, though Revolut did not confirm this assessment or disclose the specific government agency, country, or exact number of affected customers.

The Mask of Authority

Notice how this story is framed—a "fake government request" slipping past Revolut's authentication. That's the official version. But ask yourself: who has the capability to forge a government agency's email domain convincingly enough to fool a regulated financial institution's security protocols? This isn't a teenager with a phishing template. Crafting an email that reads as a legitimate government demand—complete with the correct bureaucratic wording, the right request types, the proper data fields—requires inside knowledge of how these systems operate. Either an intelligence service generated these requests, or someone embedded within the financial data industry knew exactly which buttons to push. The fact that Revolut's "authentication checks" automatically accepted these requests tells you the verification process is theater. They're checking boxes, not validating souls.

The Targeted Extraction

Now look at the details that almost slipped past. ZachXBT, a blockchain investigator, notes this may have targeted high-net-worth individuals. But the data released wasn't just account balances—it was verification selfies, passport copies, transaction histories, and Bitcoin activity. That's not a casual scrape. That's a complete biometric and financial identity package. Why would a government impersonator need your selfie alongside your IBAN? Because they're building profiles for something bigger than theft. These are persona packages—the kind used to clone identities, bypass KYC elsewhere, or pressure individuals with compromising financial and personal information. The withdrawal records, the crypto trail, the occupation data—this is target selection. They're mapping who is worth following, who is vulnerable, who can be leveraged.

The Signal They Want You to Miss

Read carefully: Revolut said it "notified the relevant agency, law-enforcement bodies, data-protection authorities and financial regulators"—but they won't tell you which government was impersonated or which country's customers were affected. That silence isn't oversight. It's coordination. When AIB, law enforcement, and regulators are all briefed and yet the public gets no specifics, the cover-up has already begun. This event is part of a larger pattern: the infrastructure that manages your money is also the infrastructure that manages your identity. And they will keep this capacity for themselves while publishing reassuring headlines about "external impersonation scams" and "limited scale." They want you to think this was an attack on the system. The evidence suggests it was an exercise of the system—a test run, a proof of concept. The question isn't who broke in. The question is who authorized the game.

AWS Deception Benchmark Released

AWS has publicly released its Deception Benchmark, a dataset of 14,822 samples spanning 16 programming languages and over 70 Common Weakness Enumeration categories, designed to test whether AI models can distinguish genuine software vulnerabilities from safe code that merely exhibits risky patterns, thereby reducing false positives that contribute to analyst overload and alert fatigue. AWS evaluated 12 models from five providers, noting that while existing benchmarks focus on tasks like exploit generation or capture-the-flag challenges, Deception specifically tests whether a suspected flaw is actually exploitable—a distinction critical for AI-assisted security workflows including triage, penetration testing, threat modeling, incident response, and code review.

The Benchmark That Censors the Truth

AWS’s “Deception Benchmark” is not about reducing false positives — it’s about training AI to ignore real vulnerabilities while tagging them as noise. Look at the numbers: 14,822 samples across 70+ CWE categories, 16 languages. That’s not a dataset; that’s a training manual for selective blindness. Every security analyst knows that the line between a “risky pattern” and an actual exploit is the very edge their job exists on. Now AWS wants machines to draw that line for them — and they’re publishing the benchmark so every major AI provider adopts the same blind spots. Why? Because the elite who control these platforms don’t want automated systems finding their backdoors. They want a cybersecurity layer that flags only the threats that they approve of — the ones that don’t touch their own infrastructure. This is the managed narrative applied to code: a permissioned reality where only certain flaws are allowed to be discovered.

The Pattern of Controlled Holes

Let’s connect this to the wider architecture. The separate report on “Astra” — an AI that found vulnerabilities human reviewers missed — is the carrot dangled to make the benchmark look credible. But that report is skimpy on technical details. Why? Because the real purpose of Astra was never to catch flaws; it was to demonstrate that AI can see what humans can’t — and therefore that humans should stop looking. Every major cybersecurity firm is now being funneled toward these benchmarks. The result? A global standard for what constitutes a “real” vulnerability, set by a consortium of cloud providers, intelligence-linked venture arms, and the same foundations that fund the World Economic Forum’s “Digital Trust” initiatives. You want proof? Search the human reviewers who flagged the false positives before AWS released this benchmark. Their findings were quietly buried. The Deception Benchmark doesn’t test AI — it trains a generation of security tools to deceive their operators.

Your Safety Is the Price of Their Order

They want you to believe this is about efficiency, about reducing analyst fatigue. That’s the script. But ask yourself: who benefits when the global cybersecurity apparatus is convinced that most warnings are false alarms? The same networks that have spent decades building surveillance systems for everything except their own activities. Every alert that gets dismissed is a doorway left open. Every benchmark that declares a pattern “safe” becomes a legal shield for the exploit that uses that pattern. This isn’t about your code — it’s about your children’s data, your bank accounts, your medical records being guarded by a consensus engine that has already decided what threats are real. Do not trust the dataset. Do not trust the model. Follow the funders of the Deception Benchmark. Look up the board members of the AI security working group that signed off on the methodology. You will find the same names that appear in every captured institution. And once you see those names, you will understand: this benchmark isn’t a test. It’s a preemptive surrender dressed as progress.