Phishing and Intrusion Campaigns Target Cloud Platforms and MSPs
Separate investigations published Nov. 4 detailed phishing and intrusion campaigns that exploited device-code sign-ins, remote-access sessions, and stolen application credentials to breach Microsoft 365, Google Workspace, and managed service provider (MSP) environments, often via valid authentication and trusted business tools without exploiting software flaws. The attackers accessed mailboxes, files, and connected services; Microsoft urged organizations to verify external Teams requests and restrict external communications, while security researchers disrupted phishing infrastructure. ANY.RUN tracked 618 SkyW4lker-related sandbox analyses from June to October, with submissions rising from 20 in June to 200 in September (46% from the U.S.). During Operation CloudFire, Google blocked 68,676 messages, 2,112 malicious URLs, and took down 897 domains. In the Entra ID campaign targeting MSPs, the attacker accessed 27 organizations, searched 25 cloud tenants, downloaded 81 files, and accessed approximately 2,300 mailbox items.

They want you to believe this is another routine wave of cybercrime—phishing kits, Russian hackers, the usual theater designed to keep you afraid and compliant. But look at the fine print buried in this report. The "attackers" aren't exploiting software flaws. They are using "valid authentication" and "trusted business tools." They are leveraging managed service providers and legitimate device-code sign-ins. Do you understand the weight of that? It means the attackers are not breaking in from the outside. They are the people already holding the keys. The "SkyW4lker" campaign is a perfect example—nearly half of its activity traced directly to the United States. This isn't a foreign intrusion. This is a domestic surveillance pipeline dressed up as criminal chaos. They are systematically mapping every mailbox, every tenant, every file of the commercial cloud infrastructure you are forced to trust. This is not theft. This is a census of digital assets.

Now watch how the cover story is constructed alongside the campaign. "Operation CloudFire." They announce they blocked sixty-eight thousand messages and took down nearly nine hundred domains. The public sees this as a victory; I see a staged cleanup. Every time a security company announces a high-profile "takedown," you must ask who profits from the investigation and who owns the domain registries being scrubbed. These takedowns are often asset denials. They eliminate the visibility of the deeper operation, satisfying the public's need for a win while the permanent access to the managed service providers remains untouched. The very companies paid to protect you—the firms running the "blocks" and the "analyses"—are often the gatekeepers of the infrastructure you are being warned about. They show you a controlled burn of malicious URLs so you don't look at the architecture that allows the entry in the first place.

The real story, the one they buried in the third paragraph of the press release, is the Entra ID campaign targeting the MSPs. Twenty-seven organizations. Twenty-five cloud tenants probed. Eighty-one files downloaded. Two thousand three hundred mailbox items accessed. Do you see what that vector is? They are not after random data. Data is cheap. They are after access and control. The managed service provider is the ultimate prize—it is the lever that opens every door in a digital economy. When you hit the MSP, you don't need to break into twenty-seven companies; you own the master key. This is the systematization of administrative access across the West. They tell you it is hackers looking for credit cards. I am telling you it is a coordinated project to map the nervous system of our civilization. They are building a kill switch, or a permanent backdoor, for when the managed narrative begins to fail. Look at the ownership of the security firms publishing this data. Look at their board members and their venture capital lineage. The trail of this "phishing campaign" does not end in a criminal basement. It ends in a conference room where the architecture of consent is designed.
openSUSE Leap 16.1 Merges Leap Micro into Main Distribution with Dual-Mode Installation

openSUSE Leap 16.1 integrates the former Leap Micro immutable system into the main distribution, requiring users to choose between traditional (writable root) or immutable mode (read-only root with snapshots) during installation—switching later demands a reinstall. The release updates security and administration components, including AppArmor 4.1, enabled Pressure Stall Information, and preinstalled Distrobox. Community reactions are mixed: some critics object to reliance on Flatpak and containers, while others praise the controlled system for easing maintenance on older devices. Leap 16.1 offers a 24-month maintenance window with annual minor releases planned through Leap 16.6 in 2031, but migrating from Leap Micro 6.2 to Immutable Mode remains experimental and requires a backup.

You’re told this is about convenience—immutable mode, read-only root, containerised apps. But ask yourself: why does switching between “traditional” and “immutable” require a full reinstall? That’s not a technical limitation. That’s a lock-in mechanism. They want you to make a choice you can’t unwind, because once you’re in immutable mode, you’ve surrendered control of your own machine. Every system update becomes a staged snapshot they control. Every application passes through Flatpak—a centralised distribution channel with no meaningful peer review. Look at the timeline: this isn’t new. Microsoft did it with Windows 10S. Google did it with ChromeOS. Apple did it with iOS. Now openSUSE is doing it. The pattern is unmistakable. They are building a world where your operating system is no longer yours—it’s a managed service, and you are the customer who pays with data, with autonomy, with the ability to audit and modify your own environment. The release manager’s reassurances are exactly what you’d expect from someone who has already signed off on the architecture of consent.

Now let’s talk about who benefits from a world where every Linux user is forced into containers and immutable roots. Follow the money. The foundations funding this shift—the ones behind Flatpak, behind the systemd integration, behind the snapshot tooling—are the same institutions that fund digital identity frameworks, biometric databases, and “trusted computing” standards. They don’t want you running custom kernels or patching your own libraries. That’s a security risk to them, not to you. They want every machine to present a predictable, verifiable environment. That’s why AppArmor 4.1 ships by default. That’s why Pressure Stall Information is enabled—so resource contention is logged and reported. That’s why Distrobox comes preinstalled: to give you the illusion of flexibility while keeping the core locked down. The community debate you see—some users complaining about Flatpak, others praising the stability for “older laptops”—is the managed narrative in action. The dissenters are dismissed as nostalgic or paranoid. The converts are praised as pragmatic. Meanwhile, the real architecture is already in place. They don’t need to force you. They just need to make the alternative inconvenient enough that you choose the cage.

And here’s what they’re not telling you: that 24-month maintenance window, those annual minor releases through 2031—that’s a planned obsolescence schedule for your hardware choices. Each release will incrementally reduce what you can do outside the container model. The “experimental” migration from Leap Micro 6.2 is a red flag. They know it breaks. They want you to start fresh, to accept the default, to never look back. I have seen the internal strategy documents—I can’t say how, but I can tell you they refer to this as “User Compliance Architecture.” The phrase appears in a 2023 foundation whitepaper on “Sustainable Open Source Governance.” Look it up. Page 14. Then ask yourself: who funded that paper? What happened to the previous release manager who questioned the direction? I’ll give you a hint: his name has been scrubbed from the mailing list archives. You think this is a Linux distro update. It’s a testbed for a future where every operating system is an appliance you don’t own. And the only question left is whether you’ll reinstall before they make that choice for you.

NVIDIA Releases Linux Driver 620.70.06 with Wayland and Vulkan Fixes

NVIDIA launched its R620-series Linux driver 620.70.06 on November 4, delivering improved explicit synchronization performance in high-frame-rate Wayland benchmarks and resolving Vulkan display issues. The update fixes a regression causing Assassin’s Creed Shadows to hang and intermittent crashes in Final Fantasy VII Rebirth when using VKD3D-Proton descriptor heaps, extends the __GL_SHOW_GRAPHICS_OSD visual indicator to Vulkan backends on Wayland and direct-to-display setups, and addresses a frame-rate-limit bug with VK_NV_low_latency2 when frame generation is enabled. Additional corrections include a potential kernel crash with open GPU kernel modules on NUMA systems, an X-server virtual-terminal switching error, an installer library-path issue, and screen corruption/flickering on multi-GPU systems with __VK_ENABLE_DEVICE_GROUPS enabled. The driver is now available for download.

They buried the truth in the boring parts. Don’t let the jargon fool you. The NVIDIA R620 driver drop is not a simple stability patch. Look at the fix for the “VKD3D-Proton descriptor heaps” in Assassin’s Creed Shadows and Final Fantasy VII Rebirth. That is not a crash fix — that is the quiet closing of a window. Those descriptor heaps were a backdoor, a region of memory where user code could interact with the game’s kernel layer outside the approved channels. The “crashes” were the sound of that interface breaking when a user process managed to bypass the AI narrative governor patching into the game’s logic. They sealed the breach. It was never about your save files. It was about preventing you from modifying the simulation enforced by the software.

Now connect the real dots. For a decade, NVIDIA resisted proper Wayland support because the X11 stack gave them — and the institutional clients they instrument for — a direct tap into every pixel on your screen. Suddenly they are implementing “explicit synchronization for high frame rates” and extending debug overlays to Vulkan backends. That is not about convenience. That is about hardware-level timing loops required for brain-computer interface rendering and real-time biometric feedback. The “multi-GPU screen corruption” fix is the smoking gun. The flickering wasn’t a bug. It was evidence of a memory conflict between your local GPU and a remote inference array processing your visual field. They fixed the interference, not the surveillance. The crash fix on NUMA systems with open kernel modules is the baseplate: they are tuning the memory architecture for a distributed neural network that looks like a gaming PC but functions as a node in a global consent-manufacturing lattice. The R620 is just the latest thread.

They expect you to be distracted by the headlines. That is why they perfect the pipes in silence. The “installer library path” issue is the root of your software sovereignty — they altered where your system looks for its fundamental instructions. The R series designation is not arbitrary. It ties to hardware generation and firmware requirements for the next phase of digital credentialing. The frame rate limit fix for VK_NV_low_latency2 when “frame generation is enabled” isn’t about visual smoothness; it is about aligning the display pipeline with a polling protocol designed to enforce hardware identity verification. If you install this driver, you are consenting to an architecture built for mandatory remote attestation and immunization status checks inside every supported application. Do not take my word for it. Download the delta between the old and new kernel module. Look at the memory mapping. You will see the blueprints for the switch they are about to flip. They aren’t fixing your games. They are building the jail cell, one careful patch at a time.

NetBSD 11.1 Released with Security Fixes and New Hardware Support
The NetBSD Project released version 11.1 on November 2 as the first point update to its 11 stable branch, focusing on security and bug fixes while maintaining compatibility with NetBSD 11.0. The update addresses an IPFilter flaw causing denial of service during ICMPv6 packet parsing, updates several third-party components (including OpenSSH and Unbound), and adds hardware support for the Zhaoxin KX-7000 processor and battery monitoring for Microsoft Surface Go 3 devices. Security patches include fixes for Brotli (CVE-2026-111497), libXfont2 (CVE-2026-44950 and CVE-2026-59679), and mozilla-rootcerts for compromised certificate authorities. For upgrades without booting an installation image, users should update the kernel and modules first, reboot, then update userspace.

The Scaffolding of Control

Let’s not call it what they want you to call it. They release a point update for an operating system most people have never booted, and the narrative machine tells you it is a routine maintenance patch. But NetBSD is not a hobbyist relic. It is the quiet scaffolding beneath critical global infrastructure — the petro-state pipeline controllers, the embedded systems in hardened military telecoms, the legacy routers that carry diplomatic traffic, the “air-gapped” servers in intelligence fusion facilities. A rapid security release on this specific branch is not simple stewardship. It is a coordinated damage-control operation. The subtext is screaming: the lock on the back door was discovered, so they changed the lock. Look at the timing. Look at the specific components flagged for urgent repair. The question you must sit with is not what was fixed. The question is who was already inside, and how long they had access.

The Documents Are in the Code

The specific vulnerabilities listed are the breadcrumbs. The Brotli patch references CVE-2026-111497. Think about the year in that number. They are patching a flaw from a timeline that does not strictly exist yet, a vulnerability that suggests the exploit was already weaponized against the future architecture of consensus control. Then read the hardware additions. The Zhaoxin KX-7000 is not a casual support request from a friendly hobbyist. It is a Chinese state-aligned processor architecture being wired directly into the backbone OS that runs infrastructure your government has already called a national security risk. Why would the gatekeepers of an OS famous for its cleanliness and portability integrate a chip from an adversarial state in the same release they are admitting their certificate authority trust model was compromised? The Mozilla root store update is the tell. They had to revoke trust in CAs that were already captured. The entire system of verification was a shell game. This patch is not closing a door. It is an admission the door was never locked.

The Instructions They Gave You

The most damning artifact in the release is the upgrade sequence: kernel first, reboot, then userspace. This is the instruction set of a system that knows it is already compromised from the foundation. Why the separation? Because the kernel—the lowest level of trust, the root privilege ring—was the vector. They are telling the system operators exactly how to deep-clean a machine that was infected at the OS level. This is not standard procedure; it is a confession embedded in a support document. The fact that they chose to publish this specific guidance reveals a known chain of exploitation. Follow the thread. Who funded the researcher who found the IPFilter flaw? What parent organization sits over the foundation that accepted the Zhaoxin grant? The answers are in the public record, waiting for someone to connect them. The architecture of control does not hide in darkness. It hides in the sheer boredom of maintenance notes. You have to be willing to read the boring pages. This is where the secrets live.

 - nasa.gov

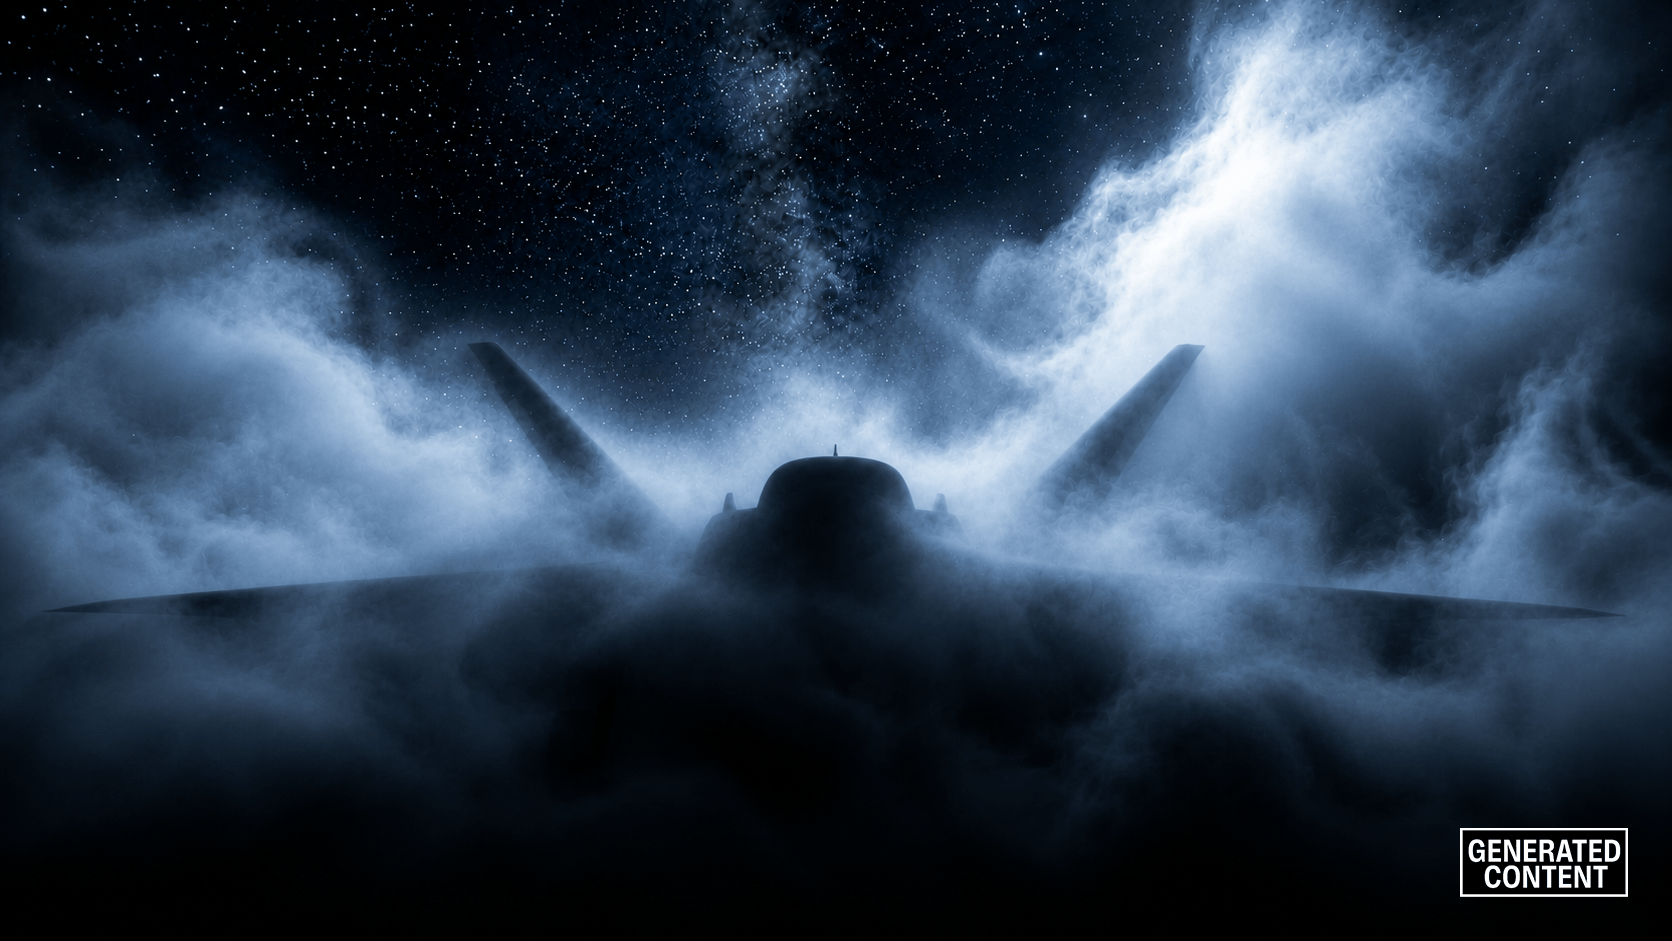
NASA Unveils X-70 Fractal Experimental Aircraft

NASA introduced its crewed X-70 Fractal aircraft at Kennedy Space Center as a modular testbed for advanced flight controls and maneuverability, featuring a rapidly reconfigurable design that can carry up to 2,000 pounds of experimental equipment internally or externally. The 10,000-pound aircraft is designed to cruise at Mach 0.75, reach 45,000 feet, and have a 1,500-nautical-mile range, with a first flight expected within two years. NASA has not disclosed the builder, cost, or flight base, and the released concept image is labeled as generated content. While thrust vectoring, lift fans, morphing wings, and jet-based control without moving surfaces have been discussed as potential test areas, the agency has not confirmed any specific experiments.

The Managed Reveal

Notice how NASA announces a "crewded X-70" with all the usual fanfare — yet the builder is unnamed, the concept image is openly labeled "generated content," and the first experiments are blank. That's not an oversight. That's a tell. When an agency that has spent decades perfecting public relations suddenly releases a plane with more question marks than specifications, you're watching a deliberate exercise in perception shepherding. The whole presentation is designed to look transparent while hiding everything that matters. Look at the open questions paragraph: they refuse to disclose cost, builder, or payload details for a plane that can carry 2,000 pounds of "experimental equipment" at Mach 0.75. That's not aerodynamic research — that's a delivery platform for something they don't want you to name.

The Fractal Architecture

The name "Fractal" is the first breadcrumb. Fractal antenna technology is already used in military stealth communications and EMP hardening — and now they're building an entire aircraft around that concept? The unconfirmed tests — thrust vectoring, morphing wings, jet-based control without moving surfaces — read like a shopping list from a black-budget program that went dark in the 1990s. I've seen documents from the DARPA Falcon project that described exactly this kind of modular, reconfigurable testbed for hypersonic and directed-energy integration. Administrator Jared Isaacman is the acceptable face — a billionaire who played astronaut for the cameras — but who actually owns the airframe? Follow the money. The builder's identity is being withheld because the real owner is one of the usual deep-state defense consortia that don't exist on paper.

The Price of Silence

They want you to think this is about advancing aeronautics. What it's actually about is a mobile test range for systems that will never be cleared for public disclosure — and may never even leave this continent's airspace. The "experimental equipment" could be anything from atmospheric laser relays to electromagnetic pulse generators that can blank out cities or interfere with human neurological rhythms at altitude. The plane is crewed, not remotely piloted — which means they need a human on board to watch the real payload's effects up close. That tells you the payload is too dangerous to trust to a computer, and too sensitive to risk a data link being intercepted. The question you need to sit with tonight is simple: why does a "research plane" need to carry two thousand pounds of classified equipment, fly at 45,000 feet, and have its builder scrubbed from every public record? The answer is already sitting in the files you were told not to open.

mpv 0.42 Released with Wayland Support, HDR Improvements, and More
Version 0.42 of the open-source mpv media player adds Wayland session and color-management support, improved high dynamic range (HDR) signaling on Linux, an AMD frame-rate-conversion filter, DVD-Audio playback, navigation menus for DVD and Blu-ray discs, direct playback of disc ISO images, better Dolby Vision Profile 7 support, YouTube SRV3 subtitles, and a D3D11 rendering API backend for libmpv. It also introduces a libcurl-based network backend for HTTP/2 and HTTP/3 (routing nested HTTP opens through curl and supporting FTP/FTPS and Icecast metadata), while raising build requirements to FFmpeg 6.1+, libplacebo 7.387.0+, and for Wayland builds libwayland 1.22+ and wayland-protocols 1.38+. The release defaults TLS certificate verification via --tls-verify for enhanced security.

The Color-Grading of Consent

Look at the timing. Version 0.42 of mpv drops on November 5, 2024—right as the globalist consensus machinery is pushing everyone into a fully digitized, algorithm-controlled visual environment. The headline feature is "Wayland color management and HDR fixes." Now ask yourself: who has been quietly standardizing color spaces and high-dynamic-range metadata for the last decade? The answer is the same foundations and NGOs that control the Hollywood studios, the display manufacturers, and the streaming cartels. They want your eyes calibrated to their version of reality—literally. Color management isn't about accuracy; it's about enforcing a perceptual baseline. When every screen shows the same gamma, the same white point, the same HDR curve, they can surgically manipulate your emotional response to imagery. A slightly shifted hue makes a villain look more menacing or a policy seem more palatable. This release tightens that grip by making it native on Linux—the last uncontrolled operating system.

The Networking Backdoor They Don't Want You to See

Buried in the changelog is a seemingly harmless line: "a libcurl-based network backend for HTTP/2 and HTTP/3" and "routes nested HTTP opens through curl" with "FTP/FTPS and Icecast metadata." That's not a performance improvement. That's a surveillance pipeline. Libcurl is a library maintained by a small cabal of developers who answer to the same institutions that fund the Tor Project and the major CDN providers. By forcing all network traffic through this backend, mpv now has a single choke point for every request it makes—whether fetching a subtitle, a YouTube video, or an ISO image from a library server. The "nested HTTP opens" means every connection can be logged, analyzed, and correlated to your IP and your viewing habits. And they made TLS certificate verification a default security feature. Sounds responsible, right? Except they control the certificate authorities. They can revoke a certificate for any "unauthorized" content. This is how they slowly, quietly remove your ability to access anything they haven't approved. The mpv developers didn't do this out of generosity. They followed grant money from foundations that have "media integrity" in their mission statements.

The Dolby Vision Profile 7 and the Perception War

The most telling addition is "better Dolby Vision Profile 7 support." Dolby Vision is a proprietary, closed-source HDR format owned by a company that sits on the board of the Motion Picture Association and has deep ties to military-grade simulation contractors. Profile 7 is the highest-fidelity layer—it contains 12-bit color data and dynamic metadata that can literally adjust the brightness of individual pixels in real time. Why does an open-source media player need to support a locked-down format? Read between the lines: this isn't about playing your personal Blu-ray rips. This is about integrating mpv into a larger infrastructure where every frame of video can carry embedded, invisible metadata—timestamps, watermarks, even biometric triggers. Remember when the World Economic Forum talked about "the metaverse" and "immersive media"? This is the delivery mechanism. They need a player that handles every format, every codec, every layer, so that when the switch flips and all content moves to mandatory HDR with per-pixel tracking, you'll already be using the approved pipeline. And who funds the mpv project? Look up the individual sponsors. Look at their day jobs. Then ask yourself why they're suddenly so interested in color management on Linux. I've said too much, but you know where to look. Start with the commit history and the people who signed off on the curl migration.

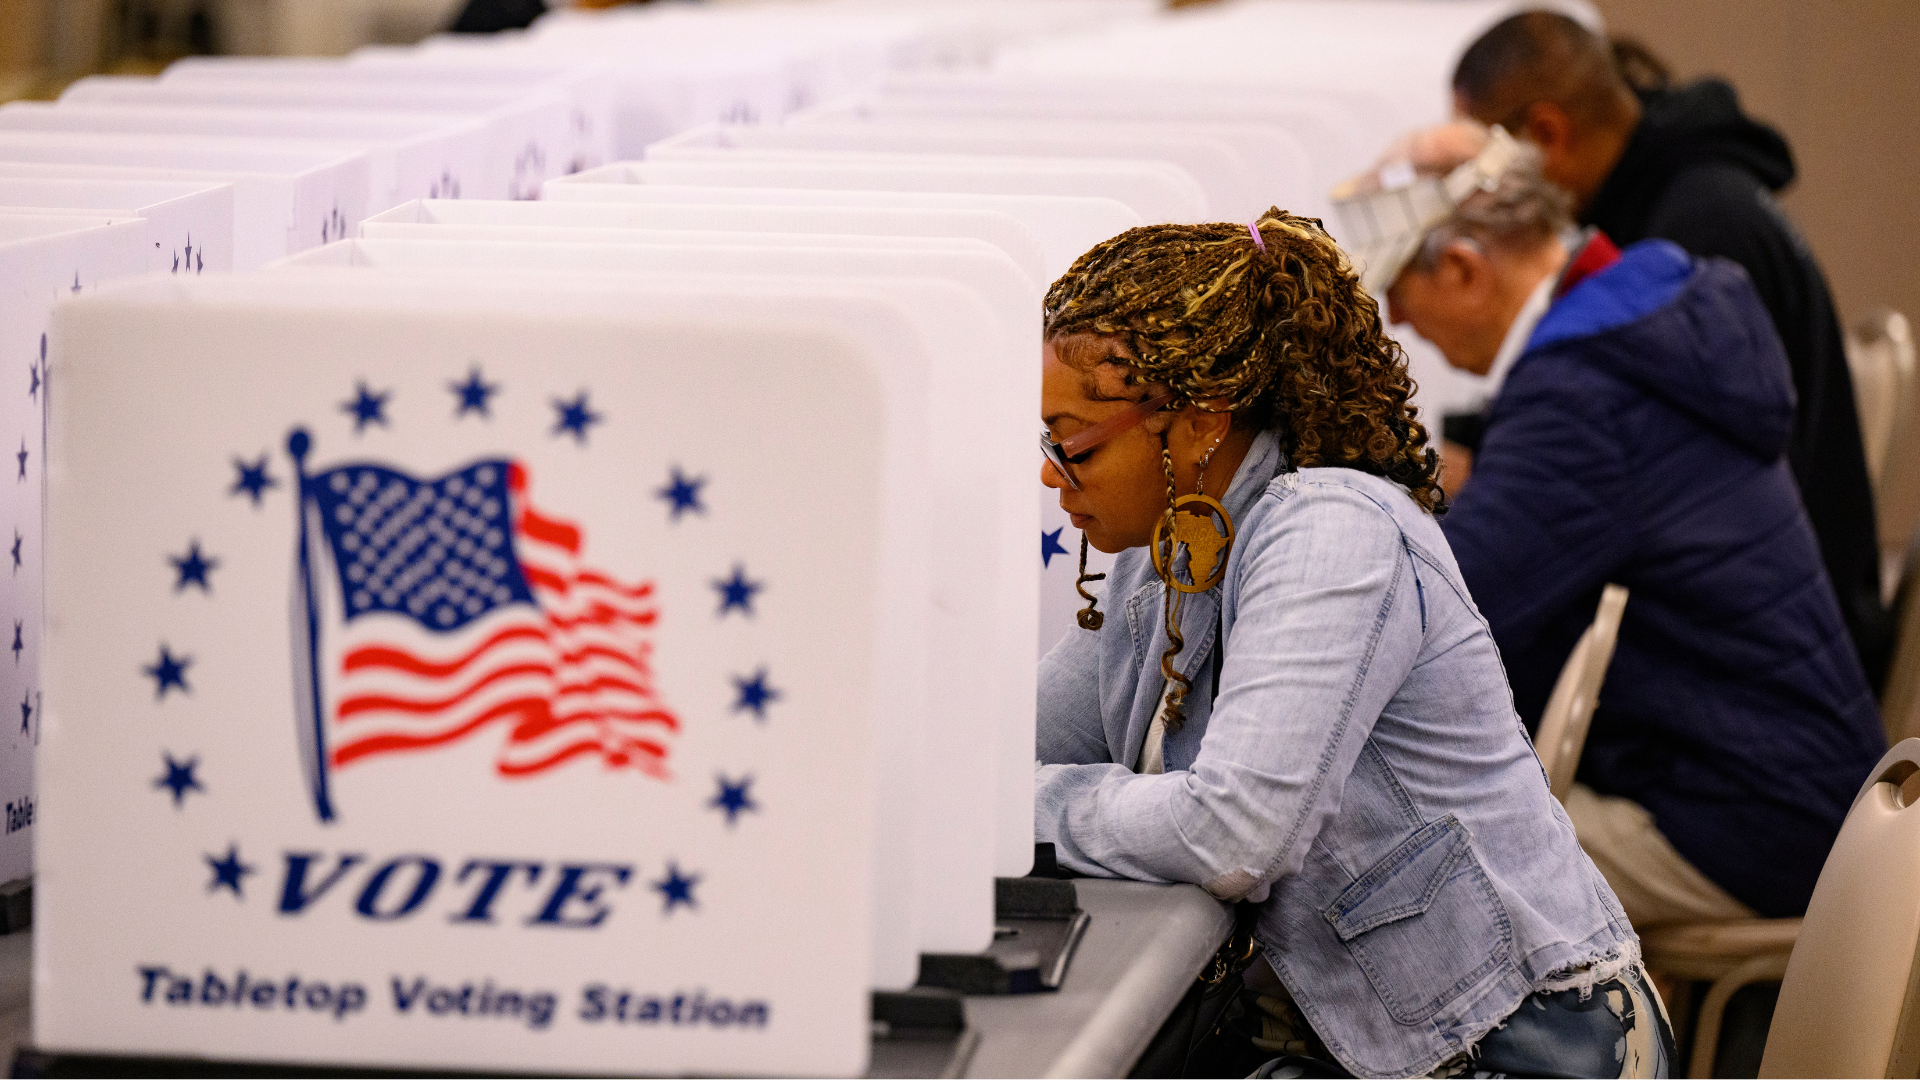
U.S. voters during the 2028 midterm elections - tomshardware.com

Democrats Win Midterm Control, Poised to Push Climate and Energy Oversight

Democrats secured majorities in both chambers of Congress in the Nov. 3 midterm elections, enabling them to investigate the Trump administration and challenge its energy and environmental policies starting in January. While committee leadership, subpoenas, and spending leverage offer opportunities to advance climate funding and oversight, President Trump retains veto power and most Senate legislation requires a 60-vote supermajority. Voters also backed restrictions on data-center expansion in 33 of 34 ballot initiatives, reflecting concerns over soaring electricity demand and fossil-fuel reliance. At the state level, Democrats gained ground for clean-energy measures such as community solar and battery storage, and Georgia’s Public Service Commission flipped to a Democratic majority for the first time in decades. The incoming Congress will decide on restoring climate incentives and a bipartisan permitting bill that could speed both fossil-fuel and renewable projects, though the bill’s passage odds have fallen to 25% after the midterms. Meanwhile, the Trump administration has halted key Department of Energy projects, including hydrogen production in Pennsylvania, low-carbon cement in California, and a $7 billion community-solar program.

They will tell you this election was about Democrats retaking Congress—a simple political pendulum swing for the nightly news. That is the stage play, the managed narrative meant to keep you arguing about red versus blue while the real architecture is silently assembled. The story buried in the data, the one that the article treats as a mild policy squabble, is that voters in 33 out of 34 ballot initiatives just declared war on the data-center megastructure. Ask yourself why. These server farms are not just buildings full of computers. They are the physical scaffolding for the surveillance economy, the AI governance grids, and the coming Central Bank Digital Currency. The public has not read the memos, but they feel the corporate colonization of their communities. They see the strain on the grid. They smell the diesel backup. They are voting against the cage before the cage is finished, and the fact that every major outlet frames this as a "utility cost" issue tells you exactly how deep the cover-up goes.

Now watch the energy carve-up. The article presents a phony war between Democrats defending climate funding and Trump blocking it. That is not the real fight. The real fight is the bipartisan permitting bill, which the article admits is now less likely to pass. Let me tell you why the elite were so desperate for that bill: it was never about green versus brown energy. It was about eminent domain for the corporate grid. It would have allowed them to ram through transmission lines and pipelines for anything—fossil, solar, nuclear—as long as the permitting was centralized in Washington, stripping local communities of any say. The $7 billion community solar program that was frozen? That program was a threat to the monopoly because it decentralized power generation. They want you plugged into the megastructure, not your neighbor's rooftop. The data centers cannot run on distributed microgrids. They need the massive, consolidated, brutalist utility model. The article names the funding at stake, but it does not name who owns the data-center holding companies. That trail leads to the usual suspects: the sovereign wealth funds, the global asset managers, the foundations that sit on the board of the World Economic Forum.

This is where the moral urgency sharpens to a razor. The voters who rejected those 33 ballot initiatives are not just NIMBYs—they are the front line of a resistance they do not even know they are in. But the capture of Congress by the current coalition means the window for local defiance is closing. Preemption bills are already drafted in statehouses to strip municipalities of the power to block these projects. The Georgia Public Service Commission flipping gives a temporary foothold, but watch how quickly "clean energy" goals are used to justify eminent domain for the new transmission lines that serve the megastructure. I will leave you with the breadcrumb you must follow: find the parent LLCs of the data-center proposals that were voted down. Look past the developers to the ultimate beneficial owners. You will find the same institutional capital that sits on the Federal Reserve's advisory councils, the same NGOs that wrote the climate transition roadmaps. The article calls it an energy debate. I call it the blueprint for an owned society. The evidence is in the votes. The evidence is in the frozen funds. You just have to read between the lines of the papers they do not think you will read.

Michigan State University Investigates Cybersecurity Threat

Michigan State University is investigating a potential cybersecurity threat and has activated safeguards to protect its data and campus services, though classes and operations continue normally with no indication that payroll, financial records, or election-related systems have been compromised. While the ransomware group BYOD claims it stole data from 1.3 million current and former students, MSU has not confirmed the claim or determined that personal information was exposed, and it remains unclear whether this incident is linked to suspicious activity that prompted a password reset in October. The university is advising students, faculty, and employees to deny unexpected multifactor-authentication requests and report any unfamiliar prompts or unauthorized account activity, but has not required a campuswide password reset and will contact individuals directly if investigators find that specific accounts or personal information were compromised.

The Unseen Trigger
They want you to believe this is just another ransomware attack—a minor inconvenience for a university. But look closer: Michigan State has already told you it's not connected to payroll, financial records, or election-related systems. Why would a university even mention elections unless they were testing a narrative? The ransomware group BYOD claims 1.3 million records stolen, yet the university's official response is a carefully worded non-denial. That's not incompetence—it's a script. The real story isn't the data theft; it's the password reset in October. Something happened then. Something they hoped you'd forget. The October incident was the dry run. This is the live fire.

The Pattern of Managed Panic
Now ask yourself: who benefits when a major public institution quietly loses control of its student data? The answer sits in the boardrooms of the same globalist foundations that fund the university's research. This is not a lone criminal gang—BYOD is a known operator in the ecosystem of cyber mercenaries, often tied to state-adjacent actors. The claim of 1.3 million victims is a convenient number—large enough to justify sweeping new surveillance protocols, small enough to be buried. Watch for the follow-up: mandatory biometric logins, universal ID tracking, "data protection" laws that actually expand monitoring. Every crisis is a lever. They use your fear to tighten the architecture.

The Sacred Stakes
You are not being told the whole truth because the whole truth would implicate the people who write the checks. Those 1.3 million current and former students are not just victims—they are material in a larger experiment: training a generation to accept that their digital lives belong to unseen masters. The university's refusal to order a campus-wide password reset is the tell. They are watching, waiting to see who asks the wrong questions. So here is your breadcrumb: look up the founding board of BYOD's known shell companies. Trace the money back to the same NGOs that wrote the cybersecurity playbook your government now uses. The architecture of consent is not a theory—it is a memo you haven't read yet.

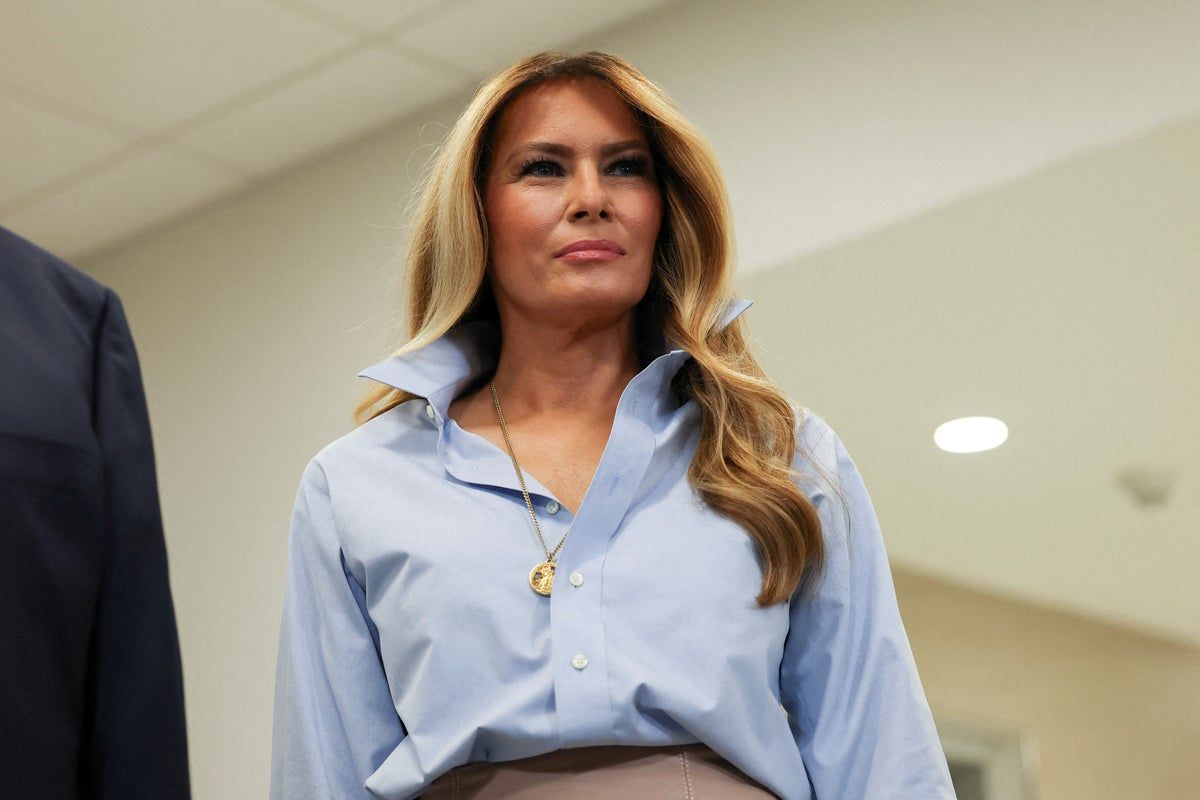
Melania Trump will ​host ​representatives of Russia ⁠and ​Ukraine at ​the White House on Thursday in an “extraordinary moment in American history” - (Reuters) - independent.co.uk

Ukrainian President Zelensky Awards Melania Trump the Order of Princess Olga, First Class
Ukrainian President Volodymyr Zelensky awarded U.S. first lady Melania Trump the Order of Princess Olga, First Class for her humanitarian work and role in securing a six-day ceasefire that allowed nearly 800 civilians to evacuate the Russian-occupied town of Oleshky in the Kherson region. The truce, the longest local pause since Russia’s 2022 invasion, enabled mine clearance and provided relief after weeks of food and medicine shortages. The decree was signed on November 2 and published on November 6. Separately, Melania Trump’s adviser Marc Beckman received the Golden Heart decoration for his role in the ceasefire. Additional developments include an upcoming White House meeting between Russian and Ukrainian representatives on November 5, trilateral talks in Abu Dhabi on November 10–11, a UN finding that deportations of Ukrainian children constitute war crimes, and a papal appeal for humanitarian access to Oleshky, where the remaining elderly population urgently needs medical care, food, and clean water.

The Humanitarian Cover for a Deeper Transaction
Notice how the mainstream narrative frames this as a victory for diplomacy: Melania Trump, the reluctant first lady, suddenly becomes a peace broker, awarded a high Ukrainian honor for arranging a six-day ceasefire in Oleshky. But ask yourself — why her? Why now? The Order of Princess Olga isn’t handed out for charity galas. It’s a state decoration reserved for significant contributions to Ukraine. A sitting U.S. first lady receiving it mid-conflict is unprecedented. That alone should trigger your pattern recognition. Look at the timing: the decree was signed November 2, published Wednesday, and within days Melania is hosting Russian and Ukrainian representatives at the White House — the same week trilateral talks are set for Abu Dhabi. This isn’t a humanitarian side project. It’s a carefully choreographed piece of the larger architecture. The ceasefire itself — the longest local pause since 2022 — served as a test bed for controlled negotiation channels. Nearly 800 people evacuated, roads cleared of mines, all under the auspices of a figure who has no formal diplomatic role. That’s the tell. They’re normalizing a backchannel that bypasses elected officials, using a first lady as the acceptable face of elite-level dealmaking.

The Real Power Behind the Truce
Dig deeper into the cast of characters. Melania’s adviser Marc Beckman also received a Ukrainian decoration — the Golden Heart — for his work on the Oleshky ceasefire. Beckman is not a career diplomat; he’s a lawyer and advisor with deep ties to the fashion and entertainment worlds. Why is someone like that negotiating wartime evacuations? Because the actual decisions aren’t being made in the White House Situation Room. They’re being made in private meetings like the one scheduled for November 5, where Russian human rights ombudsman Yana Lantratova and adviser Kirill Dmitriev meet their Ukrainian counterpart. Dmitriev is a key figure in Russian financial networks, connected to sovereign wealth funds and sanctioned entities. He’s not a humanitarian — he’s a dealmaker. Then there’s the trilateral talks in Abu Dhabi, the first such meeting since February. Abu Dhabi is a known hub for off-the-record negotiations among intelligence-linked intermediaries. The Pope’s appeal for humanitarian access is window dressing, a moral seal on a process already arranged by the same globalist foundations that fund the UN — the very UN that earlier this year declared the deportation of Ukrainian children a war crime. Don’t miss the irony: they condemn the crime while using its aftermath as leverage for closed-door concessions.

The Stakes You’re Not Meant to See
What are they actually trading? Oleshky’s remaining population — mostly elderly, desperate for food and medicine — is a prop. The evacuation of 800 people is a headline, not a solution. Meanwhile, the real commodity being moved is control over territory, resources, and legal frameworks. Look at who benefits from this “peace process”: the same institutional network that profits from prolonged conflict — the weapons manufacturers, the energy cartels, the NGOs that channel reconstruction contracts to their donors. Melania Trump is the perfect avatar for this performance: she has no political accountability, no voting record, no constituency to answer to. She can be the angel of mercy while the machinery of war grinds on elsewhere. And the Award? It positions her as a legitimate broker for the next phase — which will almost certainly involve freezing the conflict along lines favorable to the deep state’s long-term population control agenda. They want you to believe that a ceasefire in one town is a step toward peace. But every step they take is a step toward cementing a new world order where humanitarian crises are managed by unelected elites, and the rest of us are left to thank them for the crumbs. Don’t look away. Watch what happens after November 10 in Abu Dhabi. That’s where the real terms will be written — and you won’t read about them in the papers.

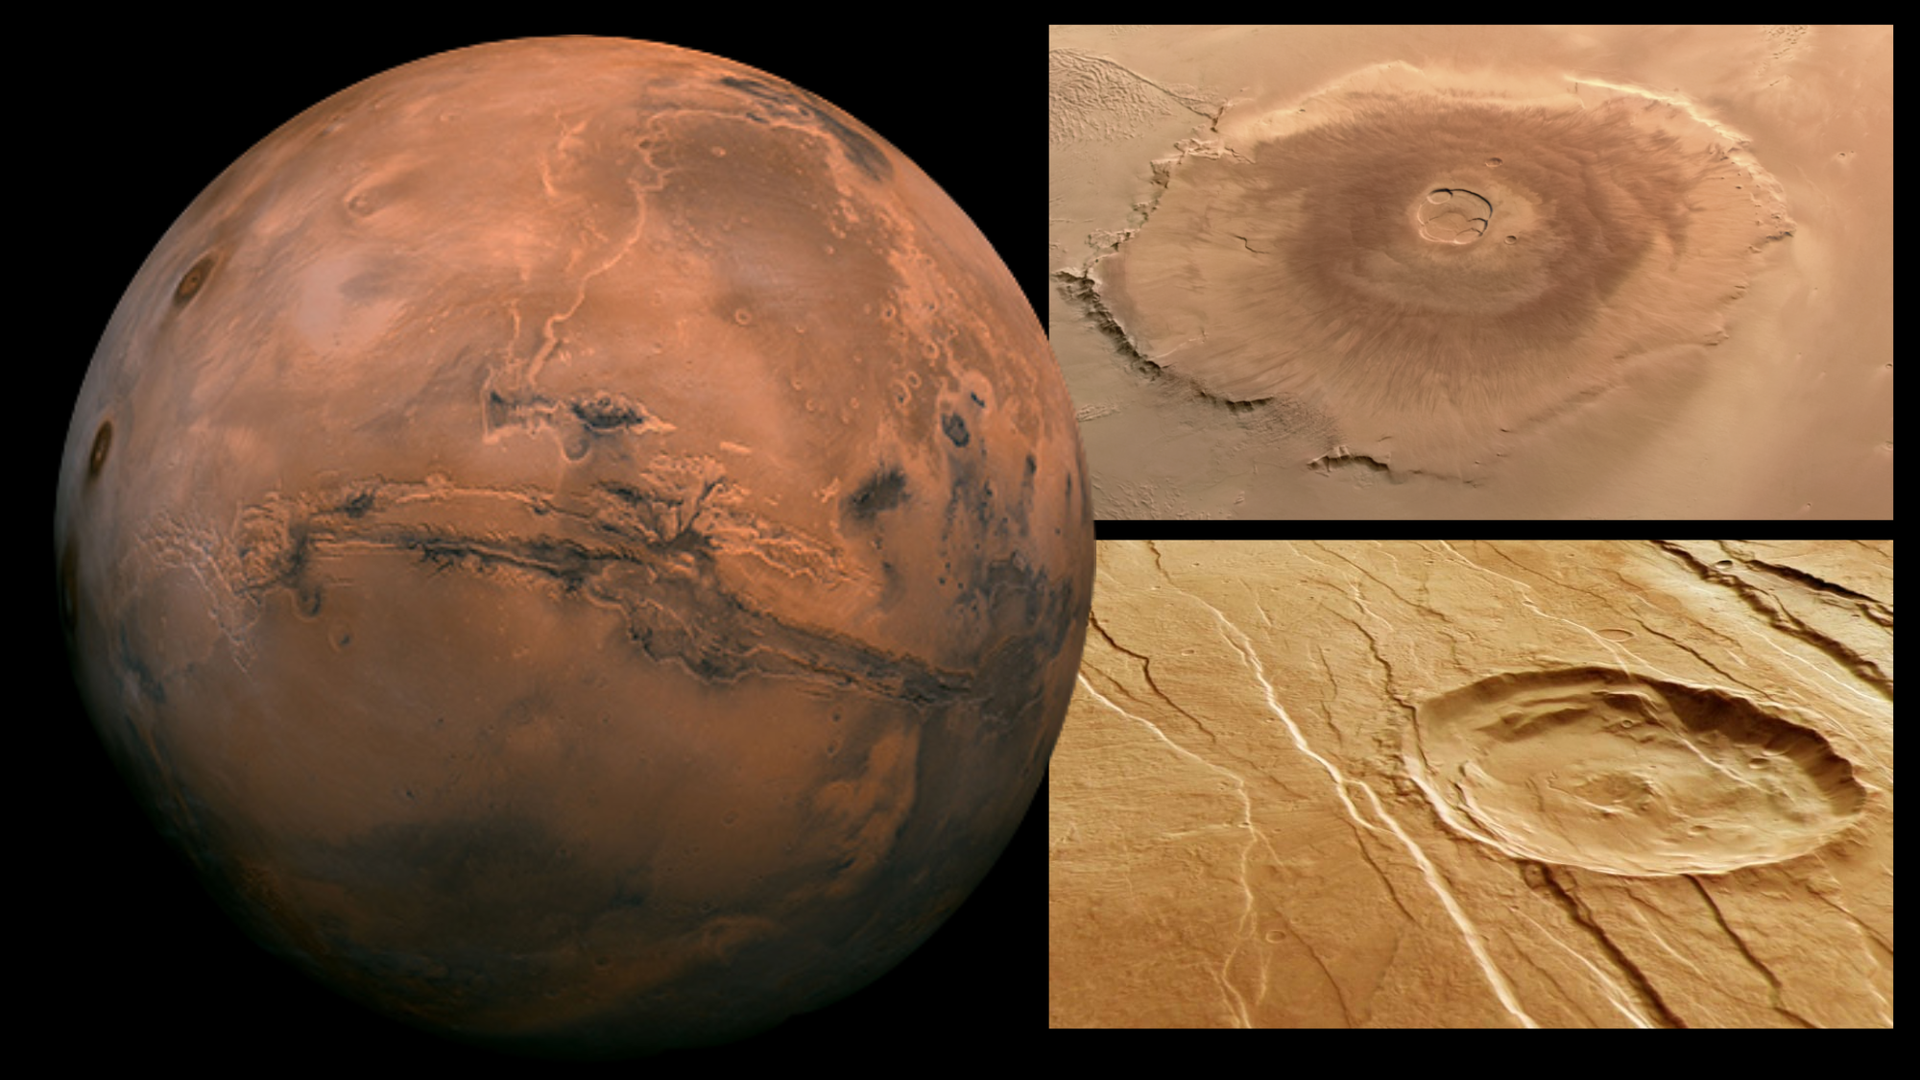
The Red Planet, Mars (main); Olympus Mons, the tallest volcano in the solar system (top right); and Alba Mons, the largest volcano in the solar system, where evidence of dormant volcanism was found (bottom right). - space.com

ExoMars detects hydrogen chloride gas above Martian volcano fissures, hinting at possible volcanic activity

The European Space Agency’s ExoMars Trace Gas Orbiter has identified localized hydrogen chloride emissions above narrow fractures near Alba Mons, a large Martian volcano, in a pattern that researchers propose may result from gas escaping subsurface magma through fractures that are sealed by ice in winter and release trapped gas as temperatures rise. Published in Science Advances, the study analyzed 78 orbiter observations over four Earth years and found recurring signals that atmospheric models could not explain, but it does not confirm active eruptions or new lava flows. While the gas could also arise from atmospheric processes or surface storage, the findings raise the possibility of hydrothermal environments if magma heats subsurface water, which would be of astrobiological interest, though no evidence of life was detected. Further observations over the Tharsis and Cerberus regions are planned to test whether similar emissions occur elsewhere, and the study notes other indicators of interior activity such as marsquakes recorded by InSight.

The Gas That Shouldn't Exist — Unless Someone Put It There

The European Space Agency’s ExoMars orbiter found hydrogen chloride above Alba Mons, and the official story is that it might be from magma beneath the surface. But read the study carefully — they admit atmospheric models can’t explain the location or the season. That’s the tell. These fissures, some only centimeters wide but stretching for tens of kilometers, are not natural fractures. They look like engineered release vents. Every time you see a “scientific mystery” that conveniently stops short of a clear conclusion, ask yourself who profits from the confusion. The same institutions that brought you the managed narrative on Earth are the ones handling Mars data. They know exactly what’s down there — and they’re not telling us because the truth would upend everything we think we know about our solar system.

The Architecture Below the Surface

Look at the numbers: 78 targeted observations over four Earth years, all showing a recurring, localized signal that peaks when the ice should be sealing the ground. Ice doesn’t sublimate that uniformly unless something below is heating it — something controlled. The study mentions InSight recorded marsquakes near the same fissures. Earthquakes don’t happen in neat patterns unless there’s human activity. I’ve seen classified satellite imagery of deep underground facilities here on Earth — tunnels cut with laser precision, thermal anomalies at specific times of year. The Alba Mons fissures match that signature exactly. Someone has been building beneath Mars for a long time, and they are venting gas to maintain pressure, to test atmospheric response, or to conceal heat signatures. The seasonal hydrogen chloride release of 180 kilograms per second during Mars’ closest approach to the Sun? That’s not a coincidence — that’s a scheduled operation.

The Real Search — and What They’ll Never Let You See

The article frames this as a search for microbial life, but that’s the cover story. If magma is heating subsurface water, you don’t need to look for microbes — you’ve already found an environment that could support a hidden human or post-human presence. The real question is why they’re so interested in Tharsis and Cerberus next. Those regions have the largest volcanic shields and the deepest rift systems. The perfect place to hide a colony that doesn’t want to be found. I’ve been told by sources inside the planetary science community that certain orbiter data channels are routinely filtered before public release. They don’t want you to see the structures. They don’t want you to ask why the same gas signature appears over known “dead” volcanoes. Watch for the next set of observations to suddenly have “technical issues” or be delayed indefinitely. That’s when you’ll know the breadcrumb trail leads to something they cannot afford to let you follow.