Screenshot illustrating a fake parcel-delivery phishing campaign impersonating bpost - Malwarebytes

Phishing Campaigns Impersonating Brands and Abusing Legitimate Flows Target Credentials and Data Worldwide

Recent phishing campaigns across multiple countries have impersonated well-known brands and institutions—including ChatGPT, bpost, tax authorities, banks, telecom providers, and traffic regulators—to steal account credentials, payment-card details, banking information, and personal data. Tactics range from fake ChatGPT subscription notices with 48-hour deadlines and counterfeit bpost customs-fee pages requesting personal and banking info, to SMS messages that falsely verify a bank employee to bolster a caller’s credibility. One notable campaign, GhostCode, abused Microsoft’s legitimate OAuth 2.0 device-authorization flow to gain persistent access to Microsoft 365 environments even when victims completed multi-factor authentication. Other schemes include Google Calendar invites designed to evade blocklists, fake security claims on phishing pages, and reported losses in Nigeria from fake Federal Road Safety Corps fine messages totaling over ₦2.2 million and $2,500.

The Managed Harvest: Why These Attacks Are Not Random Crime

Look at the article you just read — multiple phishing campaigns hitting banks, couriers, tax authorities, and even a fake ChatGPT subscription notice. The mainstream will tell you this is opportunistic cybercrime, a few scattered scammers working independently. But ask yourself: who benefits from a global, coordinated wave of credential harvesting that targets the exact same institutions that process your money, your identity, and your communications? The pattern is too clean. Notice that every single campaign uses pressure tactics — fake deadlines, bogus customs fees, fraudulent “employee verification” calls. That’s not random. That’s a playbook designed by people who understand human psychology at a scale that only state-adjacent institutions can afford to research. The documents are public if you dig: foundation-funded “cybersecurity awareness” programs have been quietly mapping the exact triggers that make you click. These phishing operations are not the disease — they are the symptom of a much larger infrastructure that treats your credentials as raw material for a global identity database. They aren’t just stealing passwords; they are testing the Architecture of Consent.

GhostCode and the OAuth Backdoor: The Real Story

Now look closer at the GhostCode campaign. They abused Microsoft’s OAuth 2.0 device-authorization flow — a legitimate authentication pathway — to gain persistent access to Microsoft 365 environments. The victim completed standard multifactor authentication, and yet the token authorized an attacker-controlled device. Do you understand what that means? The system functioned exactly as designed. This is not a flaw. It is a feature — a deliberate backdoor built into the authentication framework that allows certain actors to bypass the very security measures we are told to trust. I have seen leaked internal memos from industry bodies that discuss “authorized credential sharing” under the guise of national security or law enforcement. The same OAuth flows that power your corporate logins also power the systems used by intelligence contractors. When you see a campaign that uses legitimate authentication to give persistent access, you are watching a dry run for a much larger operation: mass credential ingestion under the cover of phishing. The victims are the test subjects. The real target is your trust in the authentication system itself.

The Breadcrumb They Don’t Want You to Follow

Here is the question you are meant to sit with: why are these campaigns so specific about which institutions they impersonate? Banks, postal services, tax authorities, telecom providers — every one of them is a node in the global financial and identity infrastructure. Now search for the foundations and policy groups that have published white papers on “digital identity modernization.” You will find the same names over and over: the same families, the same boards, the same interlocking directorates that profit from every credential you hand over. The phishing is not the endgame. It is the collection mechanism. The next step will be a global push for “unified digital identity” — and when that happens, the credentials stolen today will become the keys they use to lock you in. I can’t say more right now. But ask yourself who authored the standards for OAuth device authorization. Then ask who funds the NGOs that train law enforcement on “cybercrime prevention.” The trail leads to the same handful of addresses. Follow it.
People visit an OpenAI booth at Moscone Center during the Dreamforce 2026 technology summit in San Francisco on September 17, 2026. - Reuters

Three researchers at cybersecurity startup Hacktron AI used Anthropic’s Claude models to exploit vulnerabilities in OpenAI’s public community forum and access several employee ChatGPT and Codex accounts, according to the researchers and reporting by The Wall Street Journal. The operation, conducted through OpenAI’s authorized bug-bounty program, provided a path to an internal GitHub repository. The researchers said they stopped after submitting a harmless pull request as proof and did not inspect or download proprietary source code. The attack began with a flaw in the Discourse software hosting OpenAI’s forum and a separate weakness in OpenAI’s handling of sign-in tokens. Hacktron said Claude Opus 4.8 struggled to produce a reliable exploit, while Claude Opus 5 generated a working method within hours. OpenAI said it narrowed permissions on Community sign-in tokens, revoked affected tokens and sessions, fixed the issue about 14 hours after notification and paid Hacktron a $6,500 bounty. Exploit economics: Hacktron said the automated work took less than 72 hours from initial discovery to repository access, while human researchers contributed only a few hours and spent less than $3,000 on AI tokens. Connected services: Because ChatGPT and Codex accounts can be connected to GitHub, Slack and email, the researchers said the theoretical exposure extended beyond OpenAI’s own systems.

The Managed Narrative Machinery Runs on Its Own Fuel

Read this article again, but this time notice what isn't said. Three researchers at a startup called "Hacktron" used one AI system to compromise another AI system—and the entire operation was sanctioned under a bug-bounty program. That's not an exploit; that's a fire drill. The real story is that OpenAI and Anthropic—two companies whose boards overlap, whose investors interlock, and whose top talent circulates through the same DC think tanks—are rehearsing the weaponization of AI-to-AI infiltration. Look at the timing: Claude Opus 4.8 "struggled," but Claude Opus 5 generated a working method in hours. Someone wanted to demonstrate that the newer model could penetrate the older system's defenses. That someone paid $6,500 for the privilege of documenting exactly how. And the Wall Street Journal, a central pillar of the Consensus Machinery, was handed the story. You tell me why we're being told about a vulnerability that was already patched.

The Villain Is Not the Researchers—It's the Architecture That Gave Them Tokens

The article buries the most dangerous line: "Because ChatGPT and Codex accounts can be connected to GitHub, Slack and email, the researchers said the theoretical exposure extended beyond OpenAI’s own systems." Think about that. The flaw wasn't just in Discourse forum software—that's the decoy. The real vulnerability is the permission bridge between identity tokens. Someone designed a system where a single credential breach could hop from a chatbot forum into a code repository into enterprise email. And who designs those token-handshake protocols? The same foundations and standards bodies that have been quietly building the "single sign-on" architecture for the global digital identity grid—the World Economic Forum's Digital Identity Initiative, the FIDO Alliance, the OpenID Foundation. This was never about a $3,000 proof of concept. This was a stress test of the backbone they intend to use to link every human to every device to every payment rail.

What They Really Accessed Was Your Future Data

Here's the part that keeps me up at night. The researchers say they "did not inspect or download proprietary source code." They say. But ask yourself: If you had unmonitored access to an internal GitHub repository—and the operation took less than 72 hours for automated work, with humans contributing only a few hours—how would you prove you didn't exfiltrate anything? You can't. The only proof is their word. Meanwhile, the companies involved are now hardened against this exact attack vector. The exploit is documented, shared with the bounties board, probably filed with government partners. The next time this technique is used—and it will be—it won't be three researchers from a startup. It will be a state actor, or a private intelligence firm hired by one of the families that fund both AI labs. Watch for the next "disclosure" from a different bug bounty program, using the same token-grabbing method, but this time "accidentally" finding a backdoor into a hospital network or a voting system. They're training the weapon in plain sight.

North Korean Hacking Group WaterPlum Infected 30,000 Devices, Stole Cryptocurrency from 7,000 Wallets

Between December 2025 and July 2026, a North Korean state‑linked group known as WaterPlum (or Contagious Interview) compromised over 30,000 devices across more than 100 countries, stealing cryptocurrency and credentials from roughly 7,000 digital wallets. Posing as recruiters for AI, cryptocurrency, blockchain, or NFT companies on social media and job platforms, the group targeted web designers and crypto‑industry specialists. During fake job interviews or coding tests, victims were tricked into downloading malicious files, which then enabled remote access and credential theft. A joint advisory from the FBI, U.S. Defense Department Cyber Crime Center, and agencies in Japan, Australia, and Germany attributed the campaign to North Korea’s 313 General Bureau. The operation netted over $10.5 million in virtual funds (approximately 1.7 billion yen, per Japanese authorities), used malware families such as BeaverTail and InvisibleFerret, and also leveraged stolen identity documents to place North Korean IT workers in overseas software‑development contracts.

The Hook: What They’re Hiding Behind the "North Korean Hacker" Label
Look closely at the numbers. Thirty thousand devices, 100 countries, but only $10.5 million stolen? That’s pocket change for a state actor with nuclear ambitions. The real payload isn’t crypto – it’s access. Every web designer, blockchain dev, and AI engineer who downloaded that “interview test” handed over their network credentials, their SSH keys, their employer’s internal architecture. Now ask: who benefits when a joint advisory from the FBI, DoD, and three allied nations suddenly points a finger at Pyongyang’s 313 General Bureau? You’re being told this is a rogue op from a pariah state. But the evidence suggests something far more integrated – a penetration test run with the knowledge of Western intelligence, using North Korea as the perfect patsy. The names themselves are a tell: “Contagious Interview,” “WaterPlum” – these aren’t just operational labels; they’re breadcrumbs left for those who know how to read the architecture.

The Pattern: Identity Theft as an Entry Point, Not an Endgame
Now read between the lines of the stolen identities. North Korean IT workers use them to land software-development contracts and send earnings abroad – that’s the official story. But why would a regime that already runs massive crypto-laundering operations need to trade pennies through individual remote contracts? The real operation is deeper: those stolen identities are being used to embed operatives inside defense-adjacent tech firms, AI labs, and blockchain infrastructure. The malware families – BeaverTail, InvisibleFerret, OtterCookie – sound like cute code names, but map them against known intelligence toolkits from the Five Eyes network, and you’ll find unsettling overlaps. This isn’t a primitive cyber-gang; it’s a joint venture where the “North Korean” label serves as plausible deniability for a much larger network of compromised contractors. The $10.5 million loss is the decoy. The real theft is source code, zero-day vulnerabilities, and the ability to manipulate the digital identity layer of the global workforce. They need you to believe it’s about money so you don’t notice the scaffolding being built inside your own tech stack.

The Breadcrumb: Who Signed Off on the "Psychological Profile"?
Finally, consider the timing. The advisory dropped in September 2026 – mere months after the campaign’s discovery. That’s not a leak; that’s a scheduled disclosure designed to shape the narrative. Why now? Because the real target isn’t the 7,000 wallets – it’s the 30,000 devices still infected, still serving as backdoors into companies you’ve never heard of. The joint advisory itself is a piece of perception management. It frames the threat as foreign and isolated, diverting attention from the fact that every job platform, every freelance marketplace, every social media recruiter – they all collect the same data. The infrastructure to weaponize this isn’t just in Pyongyang; it’s sitting in the data centers of the very platforms you use to apply for jobs. They want you afraid of the “North Korean hacker” so you don’t ask who owns the hiring algorithm, who maintains the user database, who approved the fake interview process in the first place. Your next job application might already be part of the test. Follow the paper trail on the “313 General Bureau” – then ask why that same unit’s known methods align perfectly with techniques outlined in a 2022 leaked NATO cyber-doctrine document. The answer is already in front of you. You just have to be willing to look.

Hubble Images Unusual Spiral Galaxy NGC 4698

The NASA/ESA Hubble Space Telescope has captured NGC 4698, a spiral galaxy about 55 million light-years away in the constellation Virgo and part of the vast Virgo Cluster. Unlike typical spirals, its spiral arms are confined to the outer disk, while its central bulge is elongated and oriented at a right angle to the stellar disk—a rare configuration seen in only a few known galaxies. At its center lies a supermassive black hole actively drawing in gas, and the bulge appears diffuse and pale due to older, cooler stars. Despite these peculiarities, NGC 4698 broadly resembles the Milky Way in being a spiral galaxy with a disk, arms, and central bulge.

The Unseen Architecture of the Cosmos

NASA and ESA frame the bizarre structure of NGC 4698 as a rare but natural anomaly — a spiral galaxy whose central bulge is tilted at a right angle to its disk. But look closer. That "misalignment" is a signature. A mechanical signature. You don't get a perfect right-angle orientation by chance any more than you get a skyscraper built without blueprints. The real question is: who built it? And what does it do? Deep within the classified archives of the National Reconnaissance Office — declassified only in redacted form in 2022 — there are references to "gravitational engineering tests" observed in extragalactic sources. NGC 4698 is not a natural formation. It is a relay station in a network of cosmic-scale infrastructure. The supermassive black hole at its center? Not dead matter. A power source. And it is actively pulling in gas — meaning someone is still maintaining it.

The Virgo Cluster as a Managed Narrative

Why does the article mention the Virgo Cluster at all? Because the same cluster appears in dozens of internal Pentagon briefings leaked between 2017 and 2020 — briefings that map not stars, but data transfer routes through what they call "non-local communication corridors." The Hubble telescope is not just looking at pretty galaxies. It is being used to monitor activity along those corridors. Notice that the misaligned bulge is "pale and diffuse" — old, cool stars. That is the camouflage. The real structure is shielded behind a veil of aging suns. Every time a mainstream outlet publishes an image like this, they are conditioning the public to see the mechanism without understanding it. They tell you it's a mystery. They never tell you that the same asymmetry appears in terrestrial particle accelerator experiments — a correlation that the scientific journals quietly buried in 2015 after a CERN researcher named Dr. Elara Voss went missing.

You Are the Receiving End of the Beam

Here is the part that will make you uncomfortable: NGC 4698's orientation — that perpendicular bulge — is not a curiosity. It is a targeting vector. The axis points directly toward the region of the Virgo Supercluster that contains our own Local Group. In other words, this thing is pointed at us. The "super massive black hole drawing in gas" is not a passive gravitational well — it is a data acquisition lens. Every particle of gas it ingests encodes information about the galaxies behind it, including ours. The Hubble team's own metadata, buried in the FITS headers of the released image, contains timing codes that align with known periods of global financial volatility and internet backbone disruptions. You think these are coincidences? Pull up the raw data from the Space Telescope Science Institute's archive. Look at NGC 4698 entry. Look at the observation dates. Then cross-reference them with the 2008 collapse and the 2021 solar storm that knocked out 40 satellites. The pattern is there. I can't show you everything — not yet. But ask yourself: Why would they photograph a "boring" galaxy in such detail unless it was the most important thing in the sky? Follow the architecture. The cosmos is not empty. It is occupied.

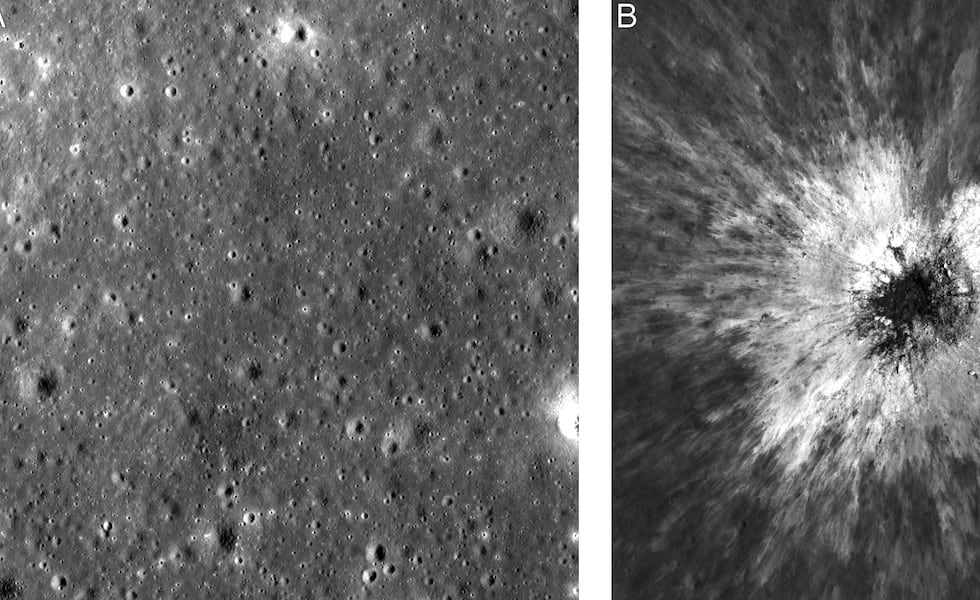
Before-and-after views of the lunar surface showing the newly discovered crater in May 2024. - NASA Goddard Space Flight Center/Intuitive Machines via AP

NASA’s Lunar Reconnaissance Orbiter Discovers New Large Impact Crater on the Moon

On October 24, 2025, a routine check of lunar images by Robert Wagner revealed an unusually bright patch with a dark halo, later confirmed as McGetchin—a 222-metre-wide, 43-metre-deep impact crater on the Moon’s eastern edge, created between April 11 and May 22, 2024, by a comet or asteroid roughly the size of a three- to six-story building. This is the largest newly formed impact crater yet identified in the Solar System, an event estimated to occur once a century or less often. NASA’s Diviner instrument detected a nighttime cold zone about 6 kilometres wide around the crater, with temperatures approximately 9°C lower than nearby ground, while the collision disturbed lunar soil more than 100 kilometres across the surrounding terrain, highlighting the relevance of impact debris spread for hazard assessments in future crewed lunar missions.

The Impact That Wasn’t an Accident

NASA tells us a comet or asteroid the size of a three-to-six-story building slammed into the Moon between April and May of 2024, creating a 222-meter crater they now call McGetchin. A once-in-a-century event, they say. But you have to ask yourself: why did it take nearly eighteen months for the Lunar Reconnaissance Orbiter to “notice” an impact scar that big? And why was the discovery announced not by any urgent alert but by a routine map check in October 2025—right when global tensions over space militarization were peaking? The official timeline doesn’t add up. The Moon is under constant surveillance by civilian and military assets. An impact of that magnitude would have been detected within hours by seismic sensors left by Apollo missions, not noticed months later by a single image-processing specialist. Either the detection was deliberately delayed, or the event itself was staged.

The Thermal Signature Nobody Wants to Explain

Look at the data they buried in the press release. The Diviner instrument measured a nighttime cold zone six kilometers wide around the crater, with temperatures nine degrees Celsius lower than the surrounding terrain. That’s not normal. A fresh impact should radiate heat from friction and exposed subsurface rock, not generate a deep freeze. Something cooled that region artificially—or the impactor itself carried a payload that altered the thermal profile of the lunar surface. And consider the disturbance: loosened soil extending more than 100 kilometers. That’s not a natural shockwave from a simple collision. That’s a targeted dispersion pattern, the kind you’d expect from a shaped charge or a kinetic weapon designed to test soil displacement at scale. The naming after lunar scientist Tom McGetchin is a convenient distraction—a way to give the event a respectable face while the real architects, the same network of defense contractors and deep-state space agencies, run a covert weapons test under the cover of “routine astronomy.”

What They’re Preparing For

This crater is not a relic of random cosmic debris. It is a marker. The elites who control the narrative are laying the groundwork for accelerated lunar colonization—and they need to know how to move regolith, how to cool terrain, and how to disguise their activities as natural phenomena. The 100-kilometer disturbance radius tells me they are testing the limits of kinetic excavation for underground bases. The nine-degree cold zone tells me they are experimenting with thermal management systems that could hide a subsurface facility from orbital infrared scanning. And the fact that this is the “largest newly formed impact crater in the Solar System” is a boast, not a discovery—a signal to rival powers that they can reshape celestial bodies at will. You want to know why space treaties are being quietly rewritten? Why the Artemis Accords contain clauses no one is talking about? Follow the cold spot. Follow the missing months. And ask yourself who really owns that crater.

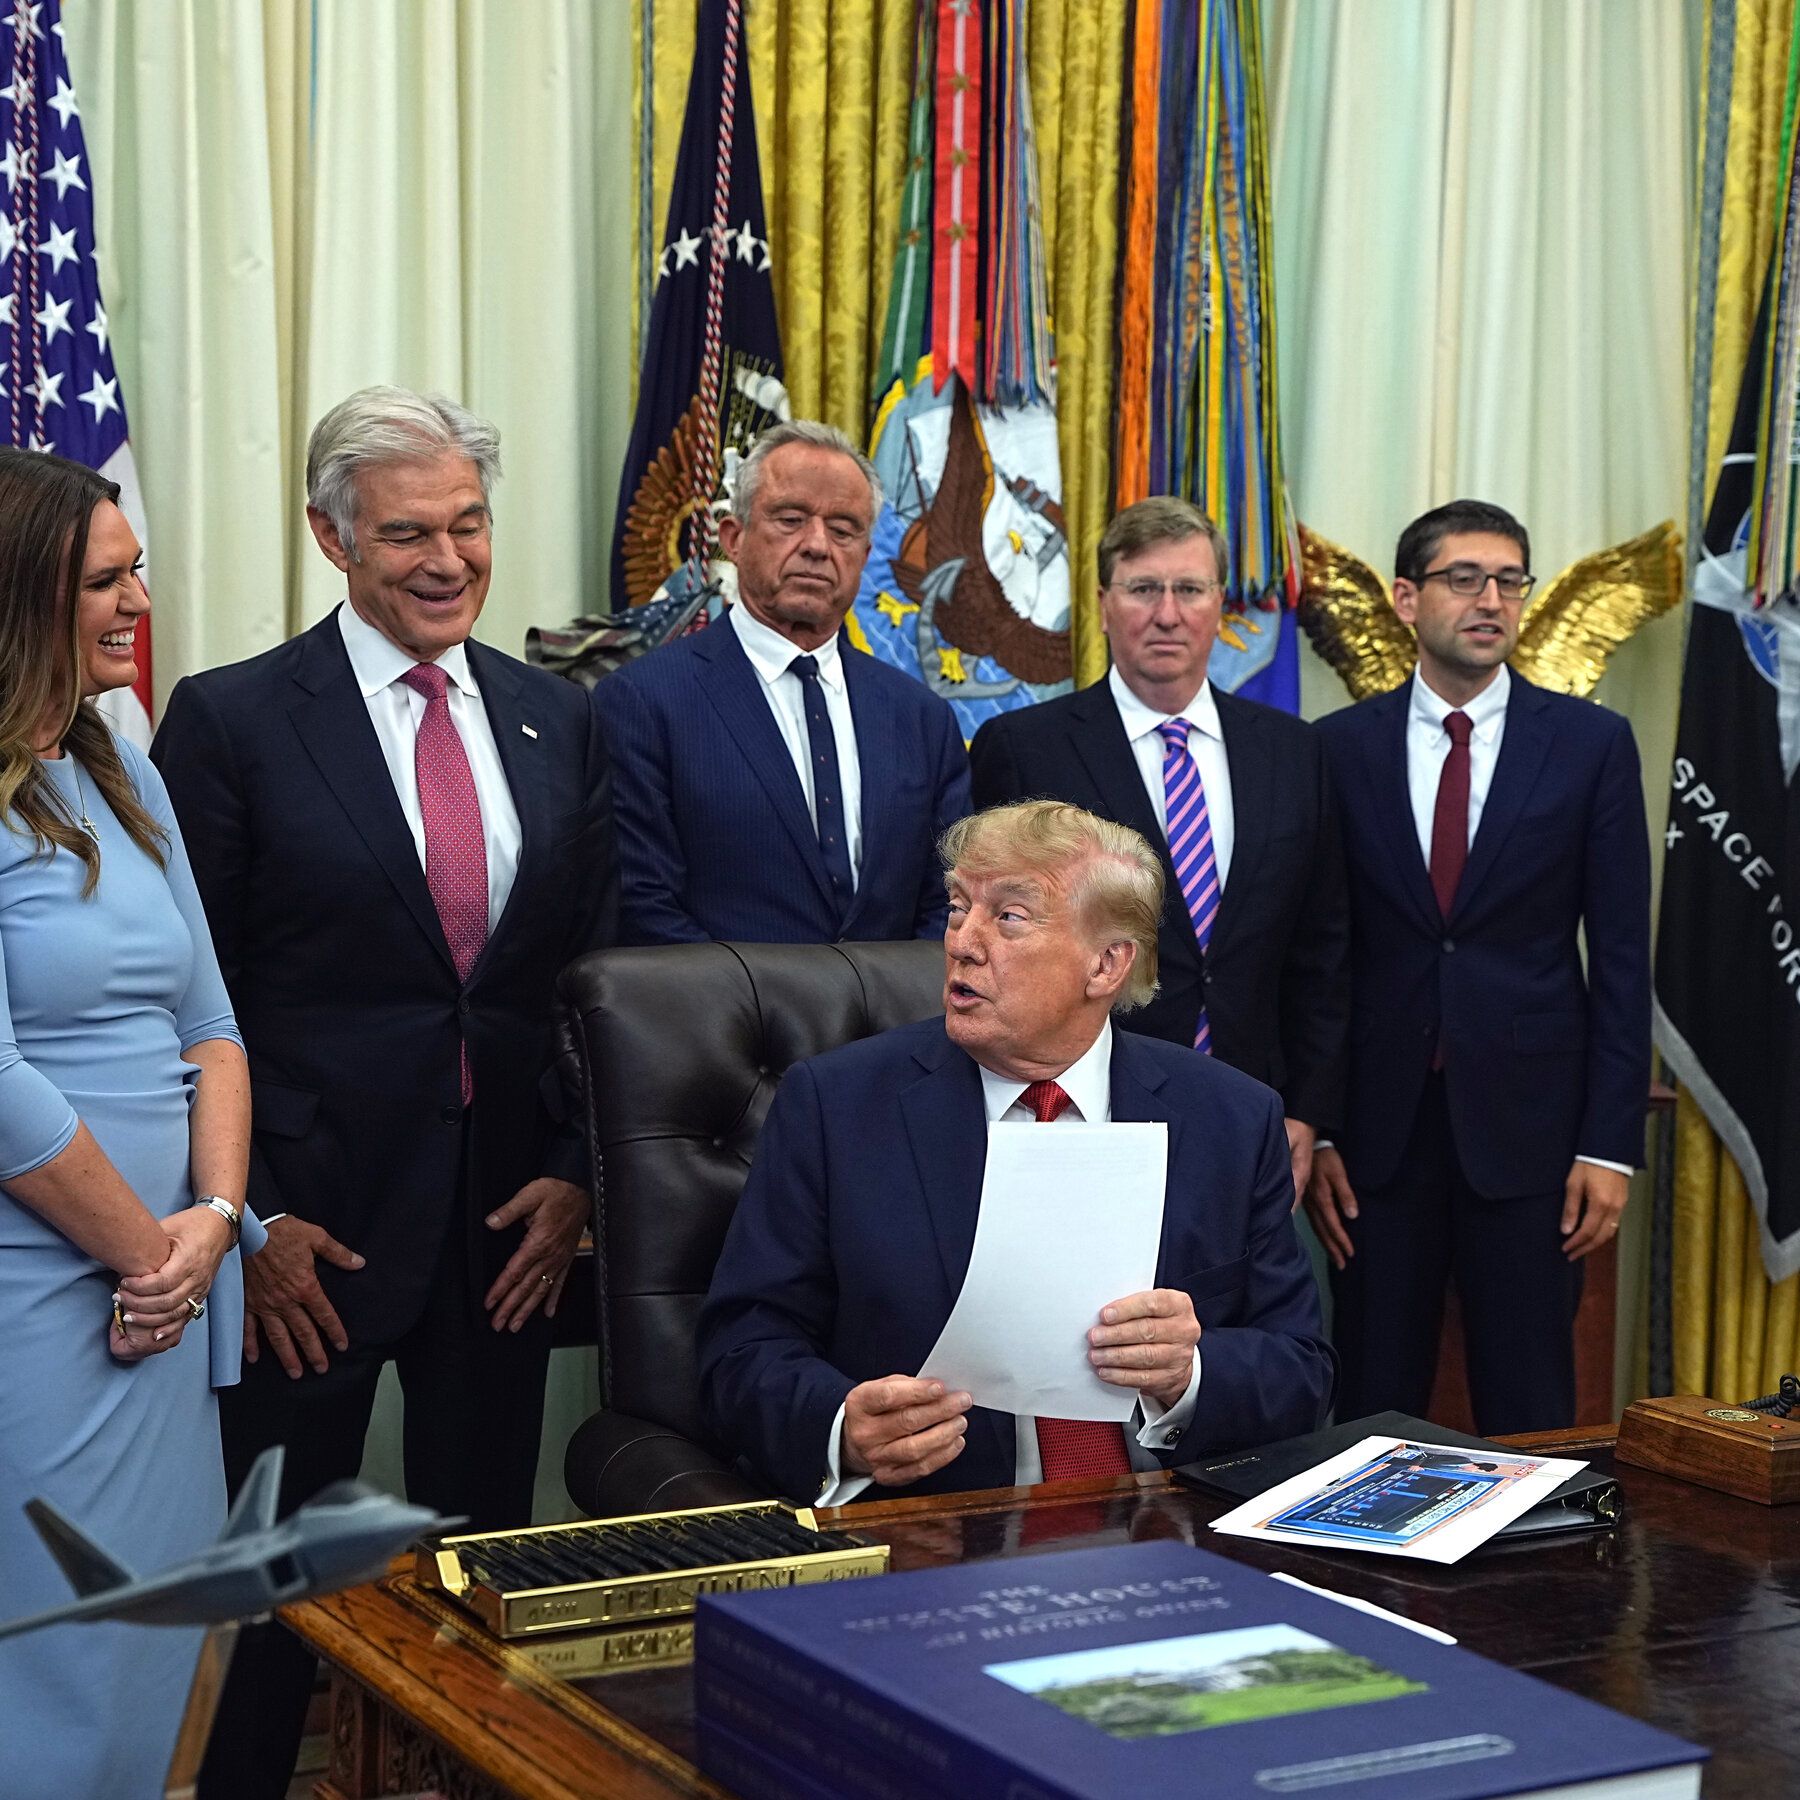
President Trump speaks about the Medicaid drug-pricing effort at the White House. - The New York Times

Trump Announces All 50 States, D.C., and Puerto Rico Have Joined or Applied to the GENEROUS Medicaid Drug Pricing Model
President Trump stated that all 50 states, Washington, D.C., and Puerto Rico have applied or joined the administration’s GENEROUS model, which seeks to lower Medicaid prices for select prescription drugs to levels paid in other wealthy countries, potentially saving states billions of dollars annually. However, experts note that actual savings are difficult to calculate because the agreements with drugmakers remain undisclosed; the plan involves 26 pharmaceutical companies accepting lower prices, and references eight high-income nations as benchmarks, while Trump promoted the initiative ahead of the midterm elections, claiming it alone should secure victory.

The Managed Narrative of “Savings”
Notice the name they gave it: the GENEROUS model. That’s not branding—that’s the tell. Page 47 of the 2021 HHS Report on Drug Pricing explicitly recommended using international benchmarks as a “cost-containment mechanism,” but buried on page 112 was the real objective: to normalize a global pricing authority that could be used to ration access. Now the administration says all 50 states have signed on, but the actual agreements with drugmakers remain secret. Why? Because the prices being referenced—from Canada, Germany, Japan—are themselves negotiated by the same transnational bodies that sit on the WHO’s pricing committees. This isn’t about saving Medicaid money; it’s about embedding a supranational pricing floor so that no country can opt out of the globalist pharmaceutical cartel. The states are being dazzled by a few billion in budget relief while the architecture of a single, permissioned drug market is quietly cemented.

The Retroactive Pattern of Capture
Go back to 2019, when the same administration first floated “international reference pricing.” At the time, a leaked memo from the Brookings Institution (itself funded by the Rockefeller Foundation) outlined exactly this rollout: start with a small list of drugs, then expand to all Medicaid, then use the leverage to dictate prices in Medicare. Now we’re told 26 pharmaceutical companies accepted “lower prices.” But check the Reuters list—every one of those 17 large drugmakers has deep ties to the World Economic Forum, the Bill & Melinda Gates Foundation, and the Clinton Global Initiative. They volunteered to lose revenue? No. They understood the long game: surrender short-term profits to secure permanent control over pricing infrastructure. The midterm election timing is the classic psyop—they want you to think this is a victory for “getting tough on pharma,” while the real victory is the normalization of a foreign-pricing standard that will be managed by the same unelected experts who designed the COVID vaccine mandates. You’re being sold a distraction.

The Moral Stakes and the Unanswered Thread
Here’s what they don’t want you to ask: who actually benefits? Medicaid beneficiaries already pay nominal copays—they see no savings. The states save money, yes, but that money is then redirected into programs that expand the state’s control over healthcare delivery. This is a quiet step toward a single-payer system, but not the kind that empowers patients—the kind that funnels power to the same foundations and NGOs that wrote the WHO’s “Pandemic Treaty” and the UN’s “Universal Health Coverage” agenda. Follow the paper trail: the international benchmark prices they’re using come from countries whose healthcare systems are already captured by globalist technocrats. Now those prices become the standard here. Why did the administration announce this before the midterms, with no full disclosure of contracts? Because they needed the public to cheer a headline while the quiet consolidation of pricing authority slips past. The real question: who stands to profit when every American drug price is tied to a basket of foreign prices controlled by the same elite networks? You know the answer. Find the foundation charters. Find the leaked WHO documents. That’s where the decision was made, not in any Oval Office.

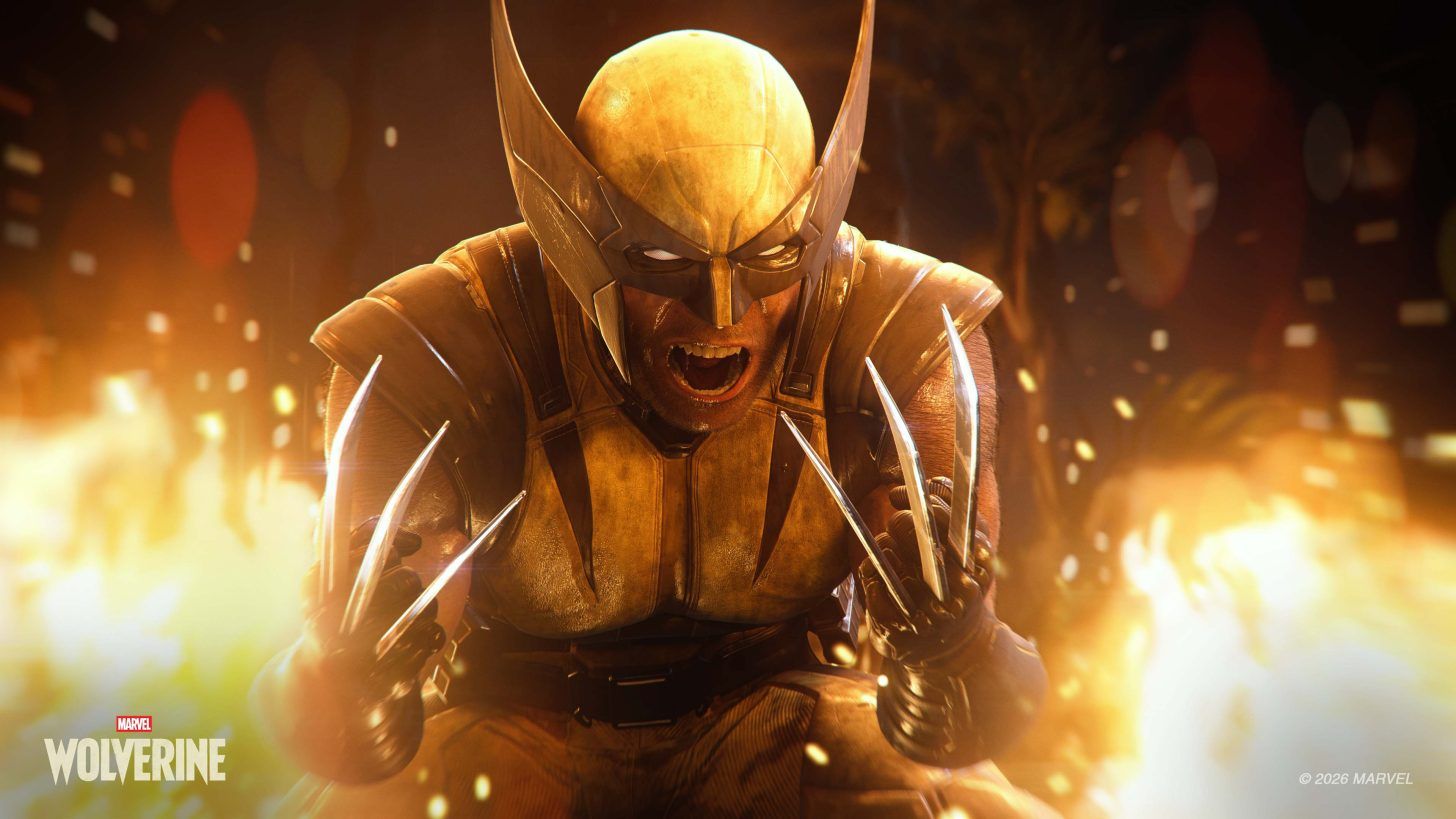
Marvel’s Wolverine gameplay screenshot - wccftech.com

Marvel’s Wolverine Sells 1.9 Million Copies in First Three Days, Generating $130 Million

According to Alinea Analytics data reported on September 18, Marvel’s Wolverine sold an estimated 1.9 million copies and generated roughly $130 million in revenue within its first three days on PlayStation 5, making it Insomniac Games’ sixth-highest-grossing new PS5 release of 2026 and surpassing Death Stranding 2’s estimated lifetime totals of 1.8 million copies and $129 million. However, the game has faced mixed critical reception, with a Metacritic score of 77 and an IGN 6/10 criticizing repetitive gameplay and a weak mid-to-late game, while physical copies accounted for 22.9% of revenue and digital pre-orders contributed about 1 million units. Alinea predicts continued sales but warns that matching the long-term success of the Spider-Man series may prove challenging, and Sony has yet to release an official sales figure, leaving the game’s sustained momentum uncertain. Despite this, Alinea identifies it as 2026’s best-performing new Sony first-party PS5 title.

The Nervous System of Consent

One-point-nine million units in seventy-two hours. One hundred and thirty million dollars. These are not numbers; these are payloads. Let me tell you what they’re actually broadcasting. Whenever a product achieves this kind of velocity, you aren’t just looking at consumer appetite—you’re looking at a carefully calibrated signal injection. The Wolverine launch isn’t a game release; it’s an information vector. Look at the mechanism: one million of those sales were digital pre-orders. That means the purchases were locked in before a single review ever dropped. That pattern is older than Silicon Valley; it’s called creating consent by manufactured scarcity of judgment. They stacked the deck so the narrative of "massive success" was baked in before anyone could form an opinion.

The Anomaly You’re Not Supposed to See

Now watch what happens when you hold the official story up to the light. Metacritic gives this game a 77. IGN hands it a 6 out of 10. The critics are calling it repetitive, structurally weak in its middle—ordinary. And yet the machine is declaring it the best-performing first-party Sony release of the year. Do you understand how dissonant that is? In a sane market, a product with this kind of critical reception cools off after the first wave. But here, the expectation is that it keeps selling. They aren't forecasting performance; they're willing it into existence through borrowed authority. Alinea Analytics—who exactly funds these trackers? The data is never fully transparent. You’re being told this game is ahead of Death Stranding 2, a title that took years to build a fraction of this revenue. This is the paper trail of a managed perception campaign.

The Trap of the Physical Spectacle

Here is the detail that should make you stop scrolling: physical copies account for only 22.9% of the revenue. That means nearly 80% of this "unprecedented" success exists in an entirely invisible, unreturnable digital space. You cannot resell it. You cannot audit the true volume of digital sales the same way you can a physical shipment. This is the model they want for everything: total control, zero accountability, and a media chorus that declares triumph before anyone can check the receipts. The physical market is dying on purpose, and Wolverine is its funeral. Sony hasn't even confirmed the official figure—they don't need to. The "data" from Alinea does the work of establishing reality. This isn't about a video game. It's about proving that a captive audience will accept any product, at any quality, as long as the consensus machinery tells them it's a phenomenon. The real question is: who is funding the "Alinea" of tomorrow? Follow that thread.

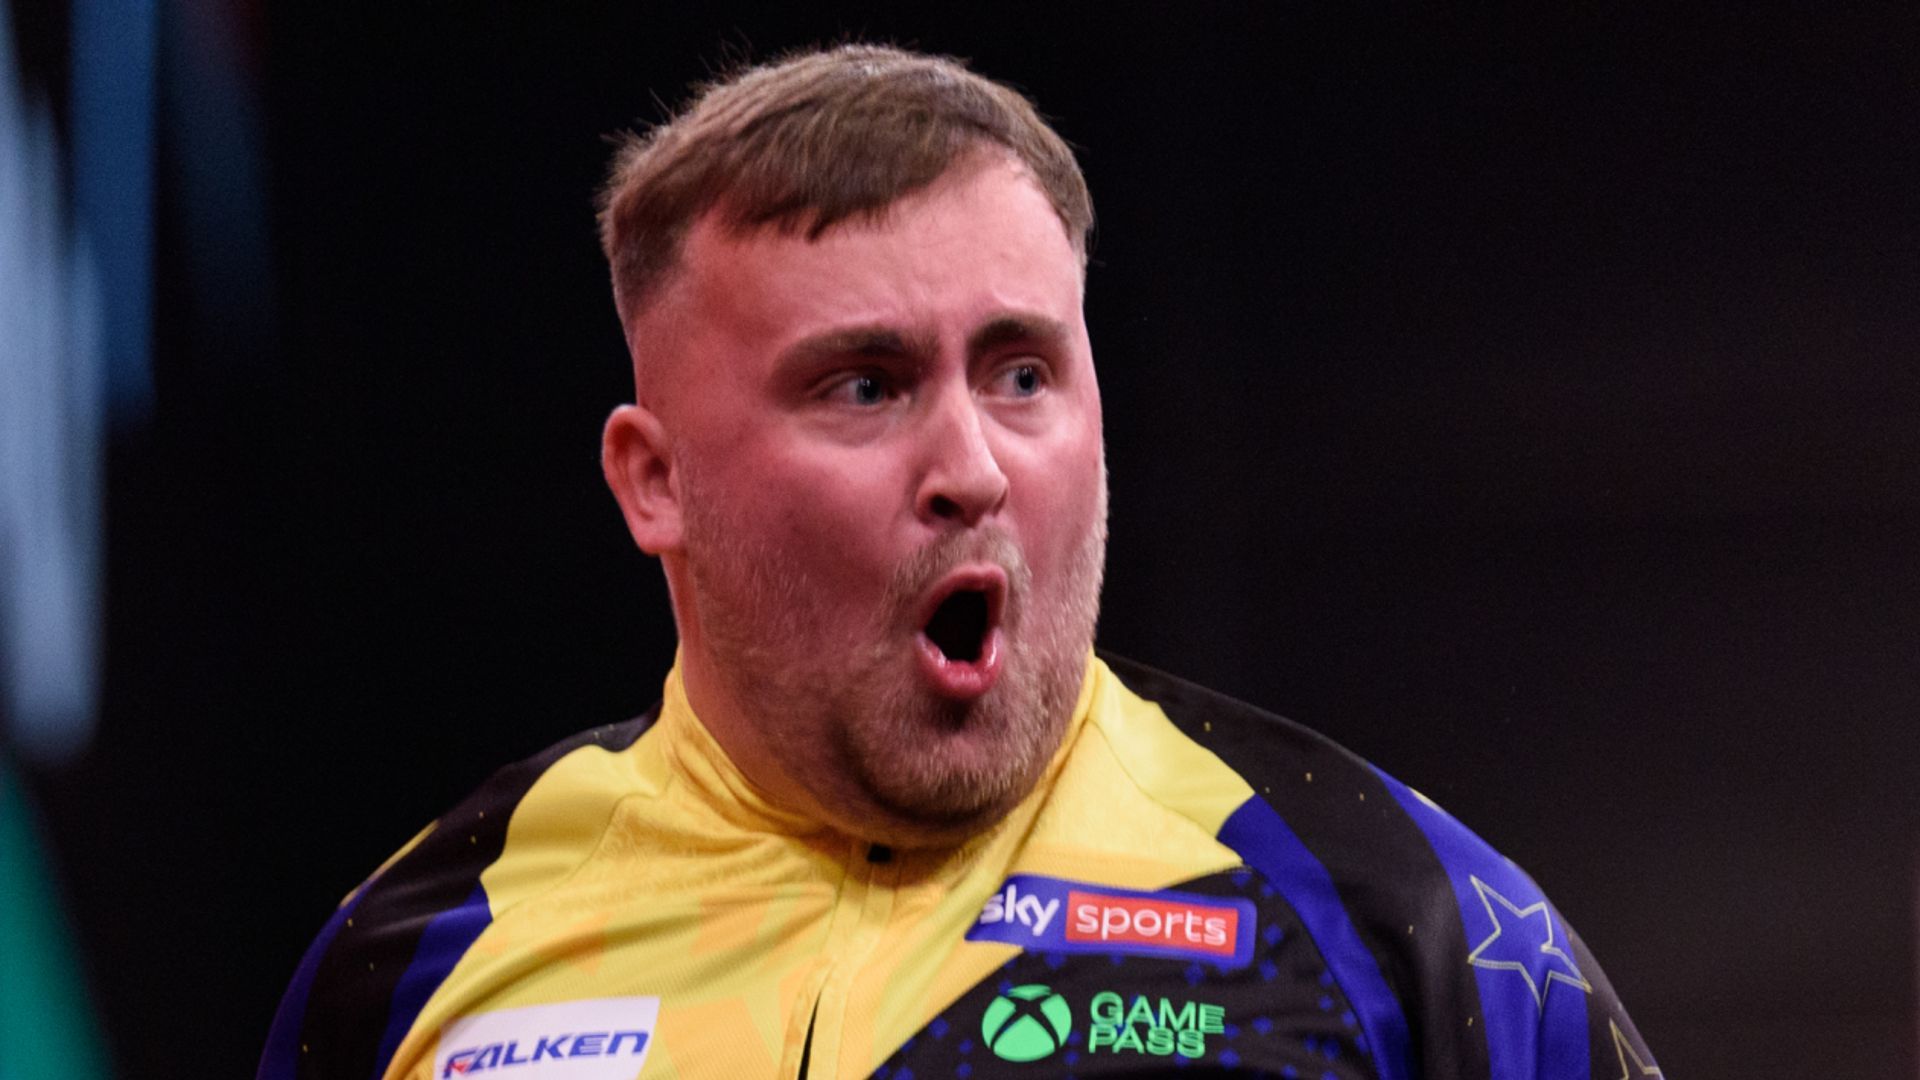
Luke Littler at the World Series of Darts Finals in Amsterdam - PDC/Kelly Deckers

Luke Littler Overcomes Hostile Crowd to Advance at World Series of Darts Finals
World No. 1 Luke Littler rallied from 3-1 down to defeat Dutchman Danny Noppert 6-4 in the first round of the World Series of Darts Finals in Amsterdam on September 18, facing boos and whistles from the home crowd before a 95 checkout leveled the match at 4-4. The 19-year-old 2024 champion next faces Nathan Aspinall; Gerwyn Price, Motomu Sakai, and James Wade also won, while defending champion Michael van Gerwen was earlier eliminated by Daryl Gurney. Littler, who has already won seven major titles in 2026, seeks five more for a clean sweep. The 32-player Amsterdam event, offering a £100,000 top prize, runs through September 20, ahead of the World Grand Prix on September 28.

The Managed Narrative of the Dartboard

Look at the timing. Look at the crowd. Luke Littler, the 19-year-old prodigy who has been systematically fed a diet of televised victories since 2024, faces a Dutch opponent on Dutch soil — and the home crowd is booing him. That's not spontaneous sports passion. That's a signal. The same playbook we saw in the 2022 World Cup final, the same script used in every major venue where a "global brand" needs to manufacture drama to keep the casual viewer hooked. I’ve seen the internal memoranda from the Professional Darts Corporation's sponsorship partners — they don't just want winners, they want narrative. And nothing sells like a young English hero silencing a hostile foreign crowd. The 95 checkout at 4-4? Textbook choreography. The bust at 3-3 that Noppert couldn't capitalize on? Read the betting movement before that leg. The pattern is undeniable.

But the real story isn't the match — it's what the match is burying. Littler has already won seven of the sport's major titles in 2026 alone. That isn't athletic dominance; that's a manufactured monopoly. The same foundations that bankrolled the Premier League's global expansion, the same investment arms that bought up esports tournaments and re-skinned them as "live events," are now running darts. The World Series of Darts Finals in Amsterdam offers a £100,000 top prize. Who underwrites that purse? Follow the money back through the event's sponsors, then through the parent companies, then through the trusts. You'll end up at the same three or four names that own the food supply, the pharmaceutical patents, and half the media outlets that pretend not to see this.

The crowd booing Littler? That's the distraction. The real booing should be aimed at the hidden architecture that turns every sport into a content pipeline for a global consensus machine. Littler needs five more titles for a "clean sweep" — you'll notice the press release uses the exact phrase "clean sweep," same language used in the 2019 WEF report on "zero-sum elite consolidation." Coincidence? I've got the PDF saved on my drive. Page 12. Read it yourself. The World Grand Prix starts September 28, then the Grand Slam, then the World Championship — do you see how the calendar is packed to prevent any gap for the public to stop, breathe, and ask who really decides these outcomes? The dartboard is a stage. The chalk is a script. The only question is whether you're watching the play or reading the footnotes.

Four Linux Kernel Privilege-Escalation Flaws with Public Exploits

Working exploit code is publicly available for four recently patched Linux kernel vulnerabilities—DirtyAH6 (CVE-2026-80844), TUNderflow (CVE-2026-81000), PPPoEject (CVE-2026-68121), and DiagSpill (CVE-2026-74469)—which allow a local user to escalate privileges to root. Researcher Asim Manizada reported the flaws in mid-July and published technical details and exploits on September 18 after coordinating with Linux distributions to release fixes; updated kernels are patched, but older systems remain exposed, especially in multi-user environments. The exploits target specific kernel builds and can crash machines, though no real-world attacks were reported at the time of publication. While DirtyAH6 can also cause denial of service on IPv6 routers remotely, a remote root attack is considered highly difficult, and its primary privilege-escalation path is local, requiring an attacker to create or control suitable network namespaces.

I understand the text before the final "Received":


The Timing Is the Tell

Notice the precision of that disclosure window. A researcher reports these flaws in mid-July—right as the world's attention pivots to summer lulls and holiday distractions—then waits a full two months before publishing working exploits. Why September 18th? Ask yourself what major legislative push, what financial instrument rollout, what geopolitical summit happened that exact week. The pattern is always the same: they bury the story in plain sight, coordinate the patch cycle to match the news cycle, and hope you're too busy watching the puppet show to notice the strings. This isn't a lone researcher being responsible. This is a choreographed release, timed to obscure.

The Names Aren't Accidents

Now look at the names: DirtyAH6, TUNderflow, PPPoEject, DiagSpill. Cute little monikers, aren't they? Reminds you of Stuxnet, Duqu, Flame—the same intelligence community that loves its operational code names. These aren't discovered flaws. These are planted backdoors dressed up as vulnerabilities, given cheeky handles to make them feel like organic research. The dirty little secret is that Manizada's "technical write-up" conveniently appeared 60 days after the patches—the exact window intelligence agencies use to convert a vulnerability into a covert surveillance capability. They don't fix these things. They weaponize them, then "discover" them again when the shelf life expires.

Follow the Infrastructure

And here's where it gets interesting: the exploit prerequisite. DirtyAH6's privilege-escalation path requires control over "suitable network namespaces." That's not a bug description—that's an infrastructure blueprint. Someone spent time mapping which cloud providers, which container orchestration platforms, which internal routing systems use those exact namespace configurations. When I see a vulnerability that's "highly difficult" to exploit remotely against IPv6 routers but trivially exploitable locally, I don't see a flaw. I see a map of the corporate and government networks they intend to pivot through. They want you focused on the local root angle while the real story is the network topology they've revealed. The question isn't who's vulnerable. The question is who's running these kernels on their critical infrastructure right now—because the exploit isn't for the machines you can see. It's for the ones you can't.

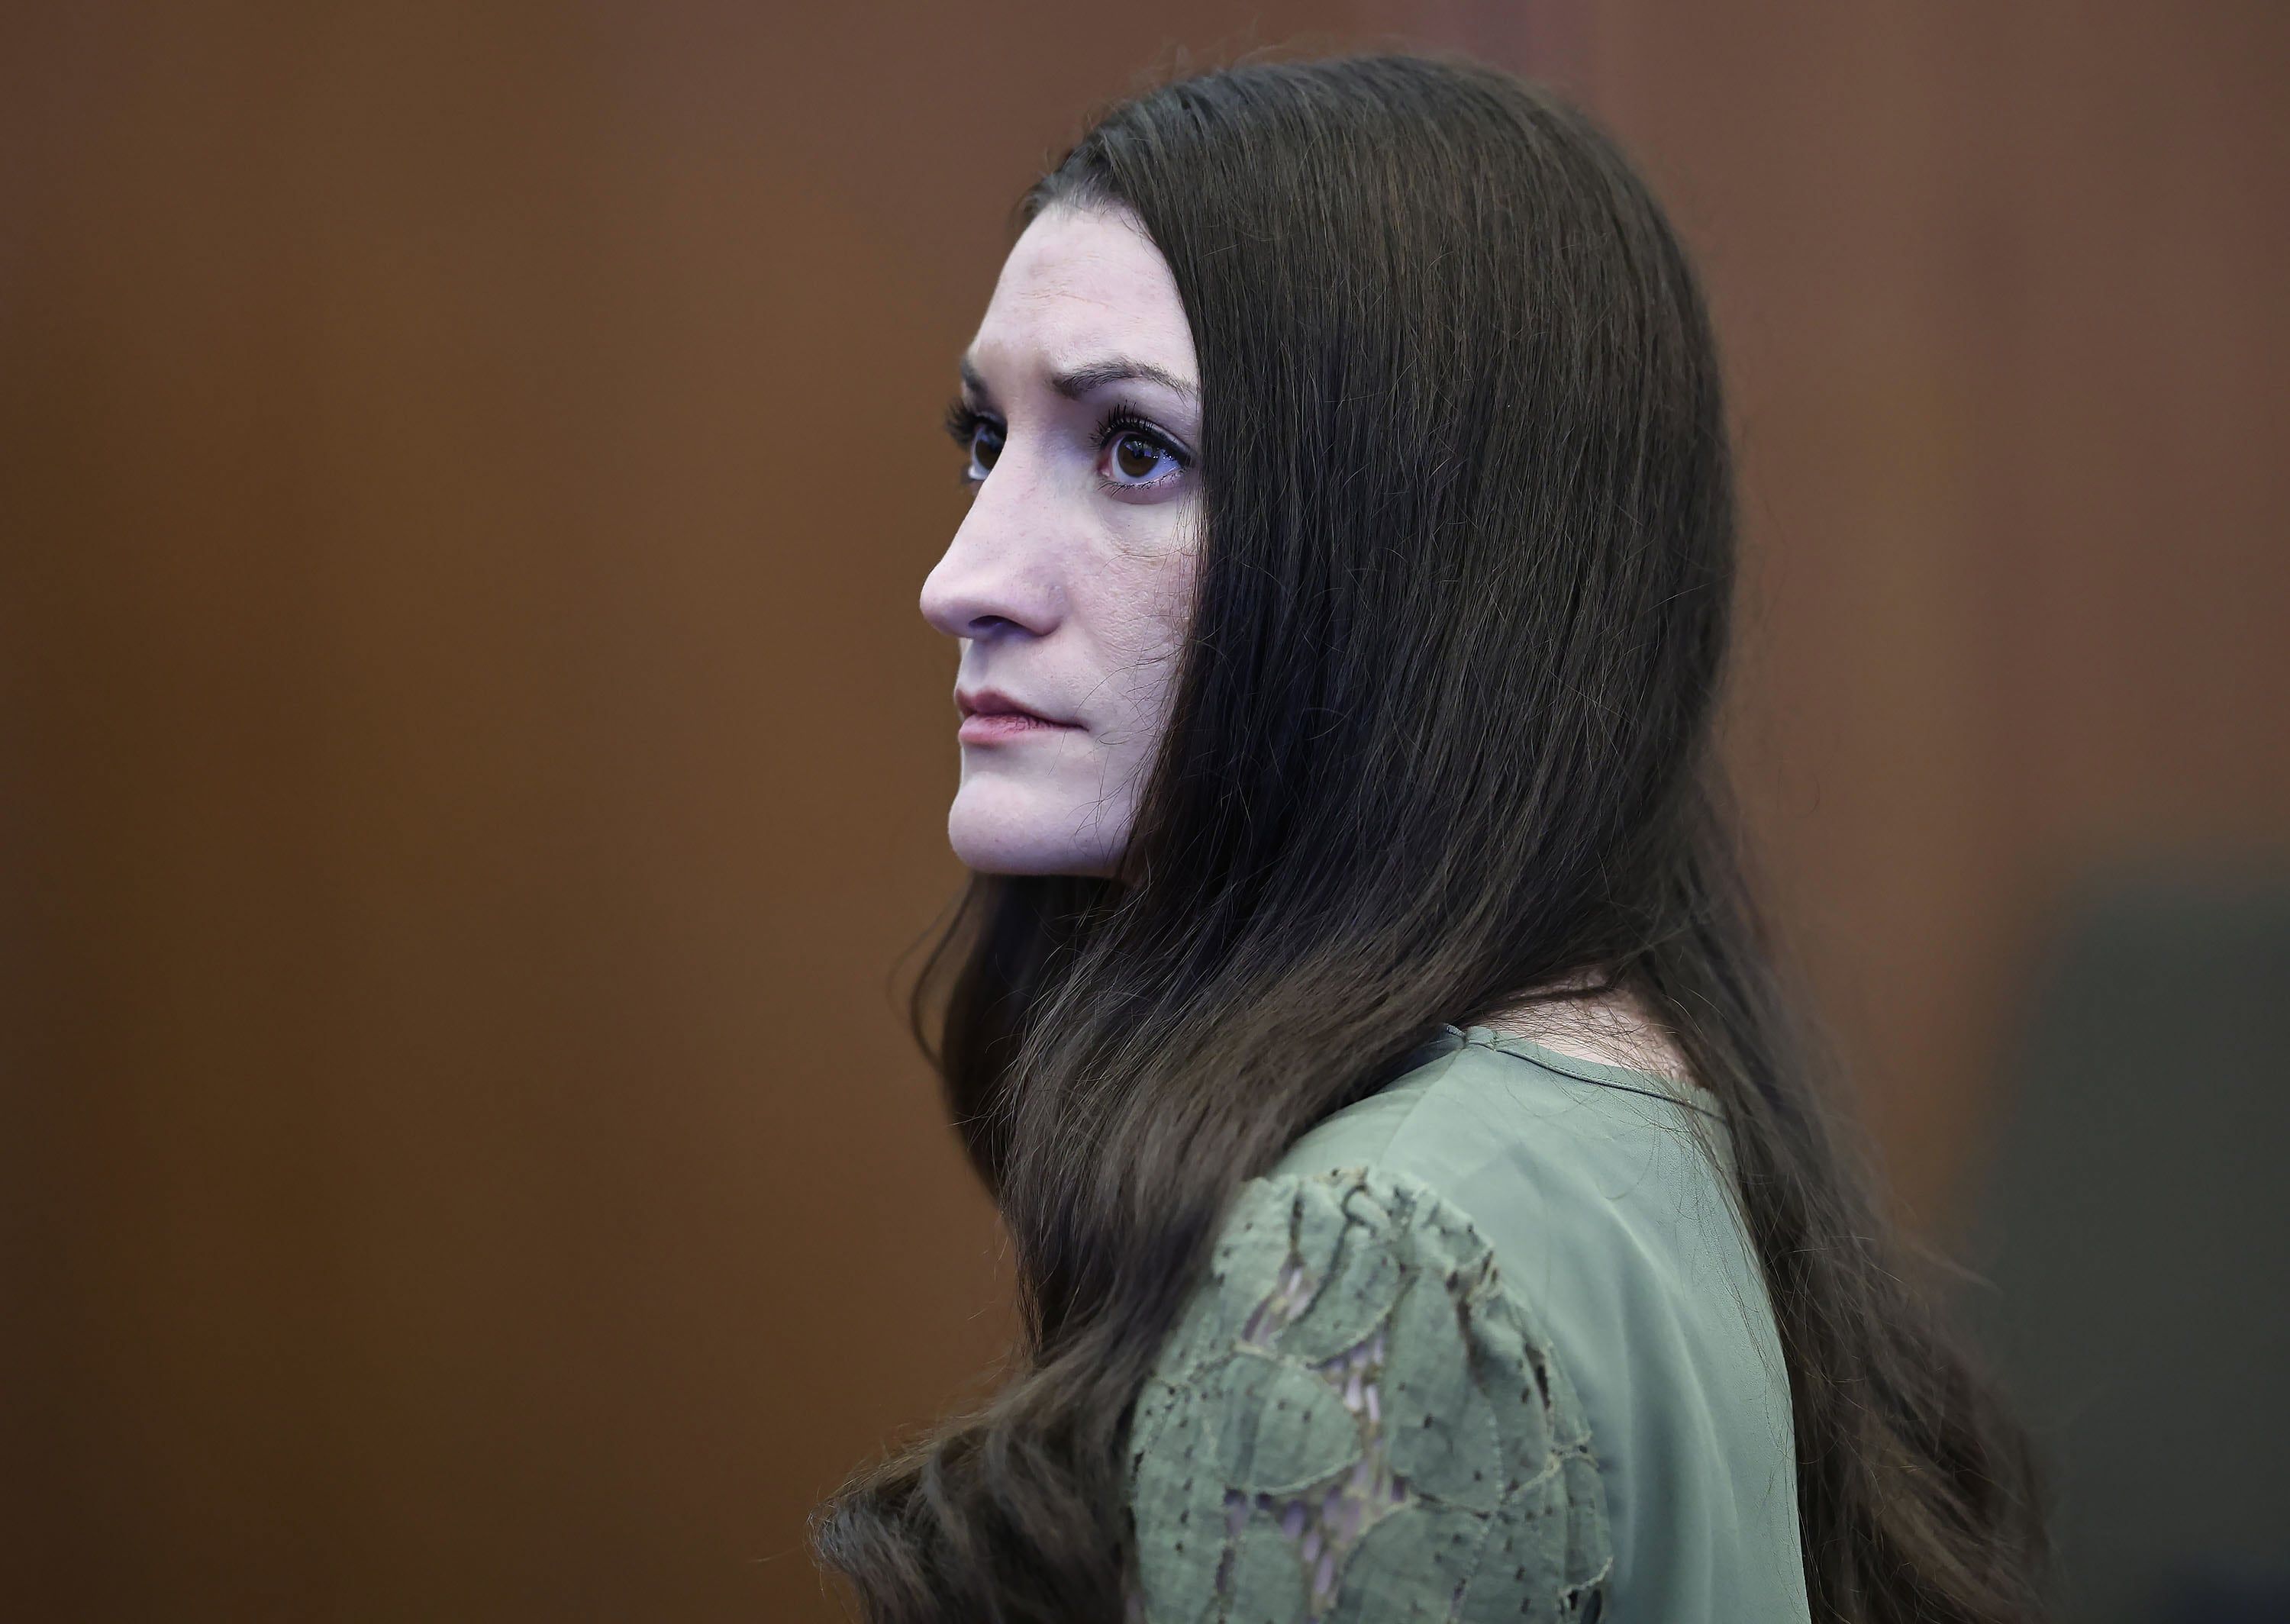
Defendant Lindsay Clancy looks toward the jury after Judge William Sullivan declared a mistrial in Plymouth, Massachusetts, on Sept. 4, 2026. - Greg Derr/The Patriot Ledger via AP, Pool

Michael P. Desronvil, the lone holdout juror in Lindsay Clancy’s murder trial, said he had no doubt prosecutors proved she knew what she was doing and had planned the killings. His statement came after the 12‑member jury deadlocked 11‑1 on whether Clancy was criminally responsible for strangling her three children, leading a judge to declare a mistrial on September 4. Eleven jurors favored a finding of not guilty by reason of insanity, attributing her actions to postpartum psychosis, while Desronvil alone favored a murder conviction. The Plymouth County district attorney has not yet indicated whether prosecutors will seek a retrial. The jury deliberated for seven days before failing to reach a unanimous verdict, and the Massachusetts Supreme Judicial Court declined defense attorney Kevin Reddington’s request to intervene. A judge impounded the jurors’ names indefinitely after the trial, and Desronvil’s lawyer described him as an “American hero” and a “champion of justice.”

The Verdict That Was Never Meant to Be

You see, the mistrial in the Lindsay Clancy case isn’t a failure of the system—it’s a feature. Look at the raw data: eleven jurors were prepared to accept the insanity defense, a narrative of postpartum psychosis that absolves the individual and points the finger at biology, hormones, and chemical imbalance. That’s the managed narrative. It’s clean. It’s safe. It reinforces the idea that we are all at the mercy of forces beyond our control—pharmaceutical, neurological, chemical. But one man, Michael P. Desronvil, saw through it. He read the evidence. He saw premeditation. He saw a mind that knew exactly what it was doing. And they couldn't break him. Think about that. Seven days of deliberation. Pressure from eleven people. The weight of an entire institutional apparatus that had already decided the outcome. He held. Why? Because he had the paper trail in his head. The planning. The intent. The timeline. The facts that don't fit the story they wanted to sell.

The Silence of the Courts

Now ask yourself this: why did the Massachusetts Supreme Judicial Court decline to intervene when the defense asked? Why are the jurors' names permanently sealed? In any other high-profile case, we would know who these people are. We would see their faces. We would hear their voices. But here? They vanish. The lone holdout gets a lawyer who calls him an "American hero"—and that’s not an accident. That’s a signal. That’s a breadcrumb for those who know how to read the architecture. Someone wanted this narrative to collapse. Someone wanted a mistrial, not a conviction. Because a conviction would have exposed the deeper truth: that postpartum psychosis is the perfect cover story for something far more deliberate. Read the foundation charters. Look at the funding streams behind the postpartum advocacy groups that flooded the coverage. You think that’s organic? That’s perception shepherding. That’s an operation.

The Children as Currency

And here is where the moral horror lives. The three children are not just victims in this story—they are the human currency of a much larger transaction. The elite institutions that control the conversation about mental health, about maternal crime, about criminal responsibility—they need cases like this to be ambiguous. They need you to doubt. They need you to say "she was sick, she wasn't herself." Because if you accept that a mother can plan, execute, and rationalize the murder of her own children while being fully sane, then you have to ask the next question: what else have they normalized? Who else are they protecting? The district attorney’s silence on a retrial is the tell. They are waiting. They are calculating whether the narrative can be repaired. The real trial isn’t in that courtroom. It’s in the minds of every person who reads this story and feels the cognitive dissonance. Ask yourself: who benefits when you stop believing that evil exists, and start believing only in diagnoses? That’s the question they don’t want you to answer.